you are viewing a single comment's thread
view the rest of the comments
[–] 59 points 2 years ago (14 children)

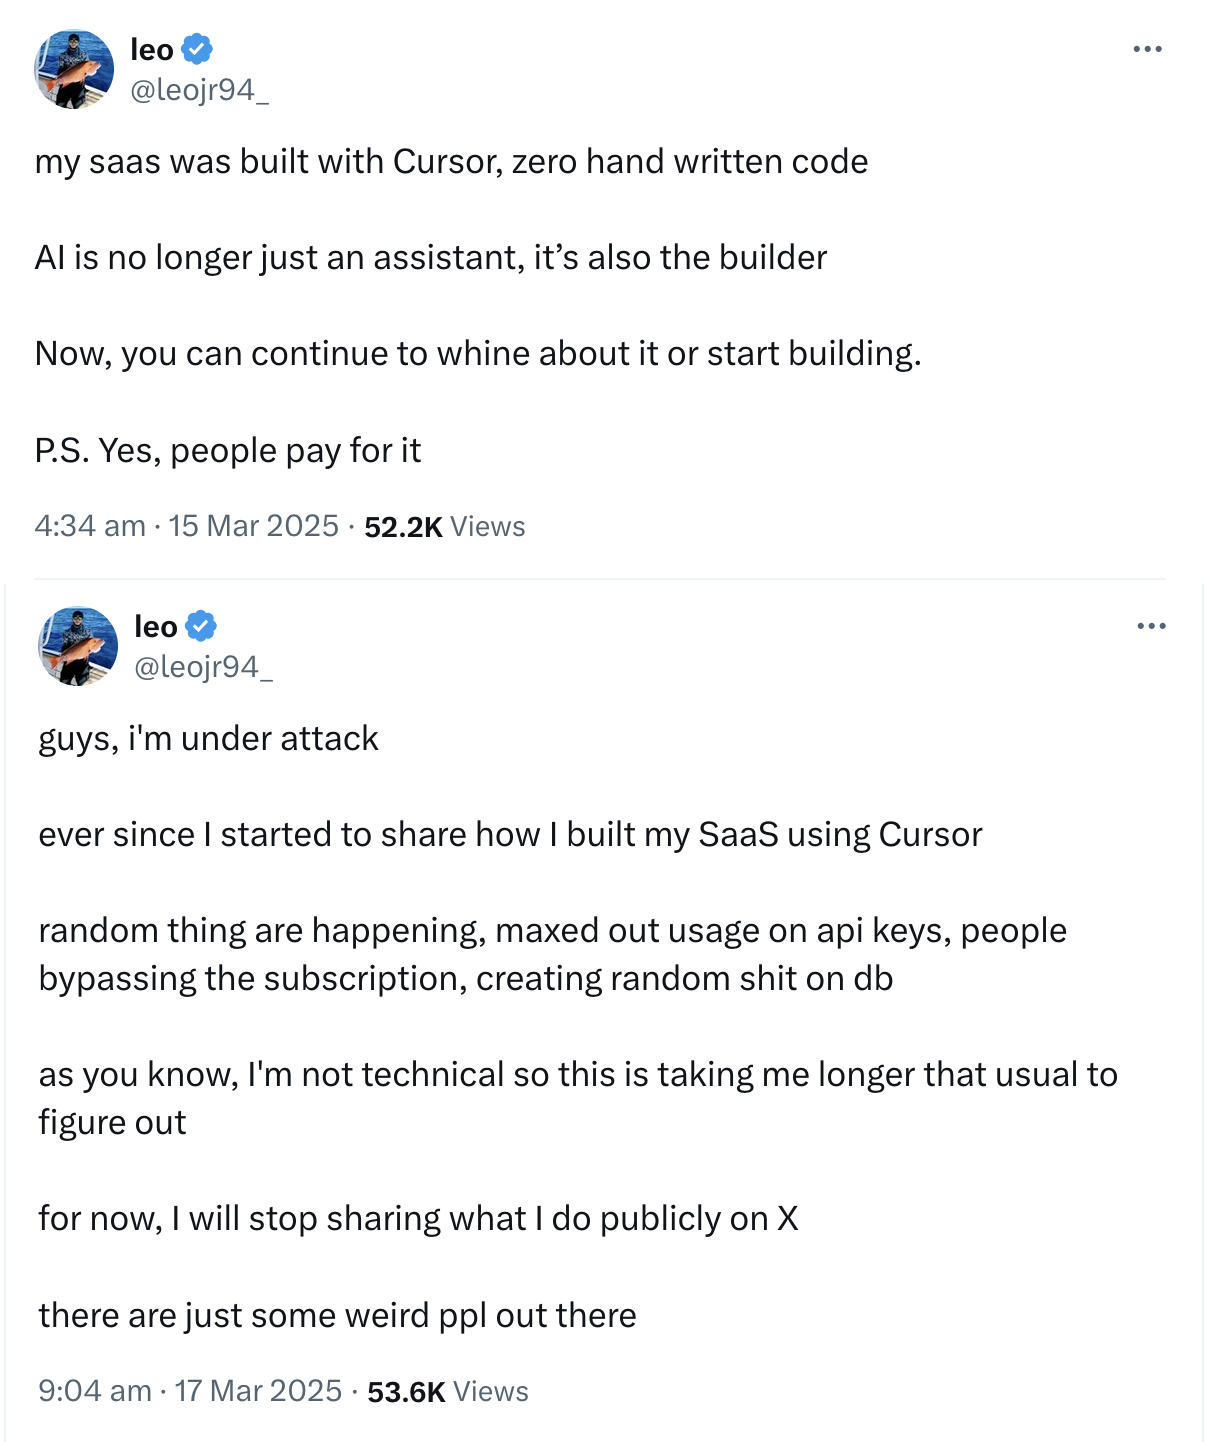
Is the implication that he made a super insecure program and left the token for his AI thing in the code as well? Or is he actually being hacked because others are coping?

  • source
  • hideshow 14 child comments
  • [–] 157 points 2 years ago (8 children)

    Nobody knows. Literally nobody, including him, because he doesn't understand the code!

  • source
  • parent
  • hideshow 8 child comments
  • [–] 46 points 2 years ago (5 children)

    Nah the people doing the pro bono pen testing know. At least for the frontend side and maybe some of the backend.

  • source
  • parent
  • hideshow 5 child comments
  • [–] 14 points 2 years ago (2 children)

    But the things doing the testing could be bots instead of human actors, so it may very well be that no human does in fact know.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 9 points 2 years ago

    Potentially both, but you don't really have to ask to be hacked. Just put something into the public internet and automated scanning tools will start checking your service for popular vulnerabilities.

  • source
  • parent
  • [–] 8 points 2 years ago

    He told them which AI he used to make the entire codebase. I'd bet it's way easier to RE the "make a full SaaS suite" prompt than it is to RE the code itself once it's compiled.

    Someone probably poked around with the AI until they found a way to abuse his SaaS

  • source
  • parent