1


Hello everyone! Mods here 😊

Tell us, what services do you selfhost? Extra points for selfhosted hardware infrastructure.

Feel free to take it as a chance to present yourself to the community!

🦎

2


CWA is an eBook manager, and it is popular in the selfhosted book space. Please see the changelog link for the full summary, it is well organized and so I didn't copy it here.

3


I have messed around with NUT to trigger a graceful shutdown of my home server running Ubuntu Server. I have struggled with setting NUT up on bare metal, but would like a gui anyway. I saw PVE-UPS which looks good, but I think but I think it is meant for Proxmox. Any alternatives, or a spin of PVE-UPS for docker compose anybody know about?

4


I'm not affiliated with this in any way but saw it posted at the other place & thought fellow Lemmyzens might like to take a look.

I always find it quite hard to answer "favorite" apps as some infrastructure critical self hosted apps aren't as sexy as others which sit front & centre so I feel they often don't seem to get as much credit or attention (such as NGinX/DuckDNS compared to Immich/Jellyfin etc)

Hi everyone,

Like in previous years, I'm running a survey about self-hosting. The focus is on your favorite self-hosted apps, but there are plenty of other (optional) questions too. The top five app lists are free response fields, you don't have to select the suggestions.

Link to take the survey:

https://survey.deployn.de/s/self-host-2026

Last year's results

More info:

  • The survey is anonymous. Like last year, results will be published in aggregated form. I'm currently planning to publish them in December.

  • It takes about 10-25 minutes.

  • Some of you asked for more questions in the comments. I added a lot at first, then realized it took 45 minutes to fill out properly. So I threw some out again, but there are still quite a few. The survey now has a core section that mainly covers the MVPs (your 5 favorite apps), and you can switch on other modules if you want. Almost every question is optional and can be skipped. If you answer everything at a reasonable pace, it takes around 20 minutes.

  • The proprietary survey tool caused new problems every year, so last year I switched to HeyForm while the survey was already running. That wasn't ideal for my purposes either, so this year the survey runs on a new app. It should also make entering your apps faster.

  • It's still easier to fill out on a desktop computer.

Thank you in advance for participating.

5


It took me a while to figure out why many of my self-hosted services were intermittently failing to connect on my phone after updating to Android 17. I eventually figured out there's a new ACCESS_LOCAL_NETWORK permission which means the "Nearby devices" permission is now required to access devices on the same network subnet. For an avid self-hoster, this can be quite a bit.

I had my DNS configured so my public-facing server resolved to a local IP address when on my LAN. This meant that my web, immich, xmpp, NTP, jellyfin and DoH servers all resolved to a local IP address on wifi. On Android 17, it all broke without warning. No error messages. No asking for extra permissions. Just silent packet dropping.

I've solved it by configuring my public-facing services to resolve to my external (static) IP address, even when inside the network. I couldn't make any internal services resolve to the external address (SMB, CUPS etc) because they are (obviously) not bound to my WAN interface.

I get why the change was made. A lot of apps were snooping around people's networks to gather intel. A potentially massive privacy violation.

Has anyone else had this issue? Is this the cleanest solution?

6
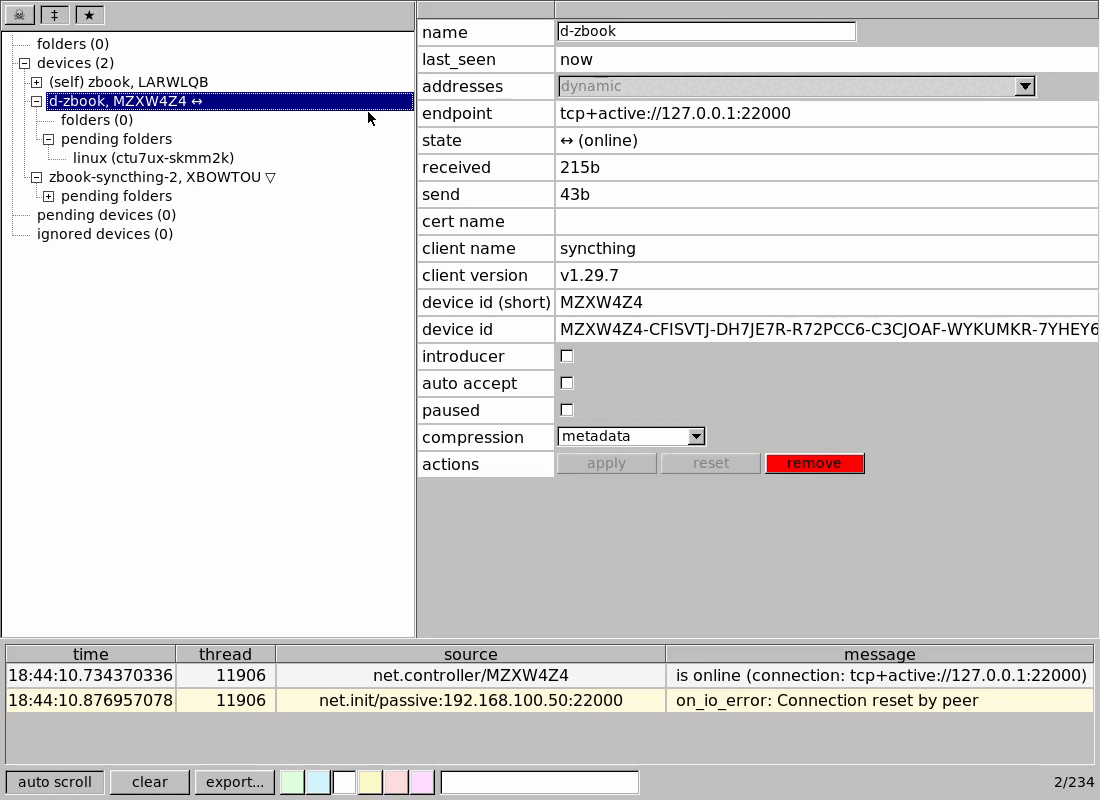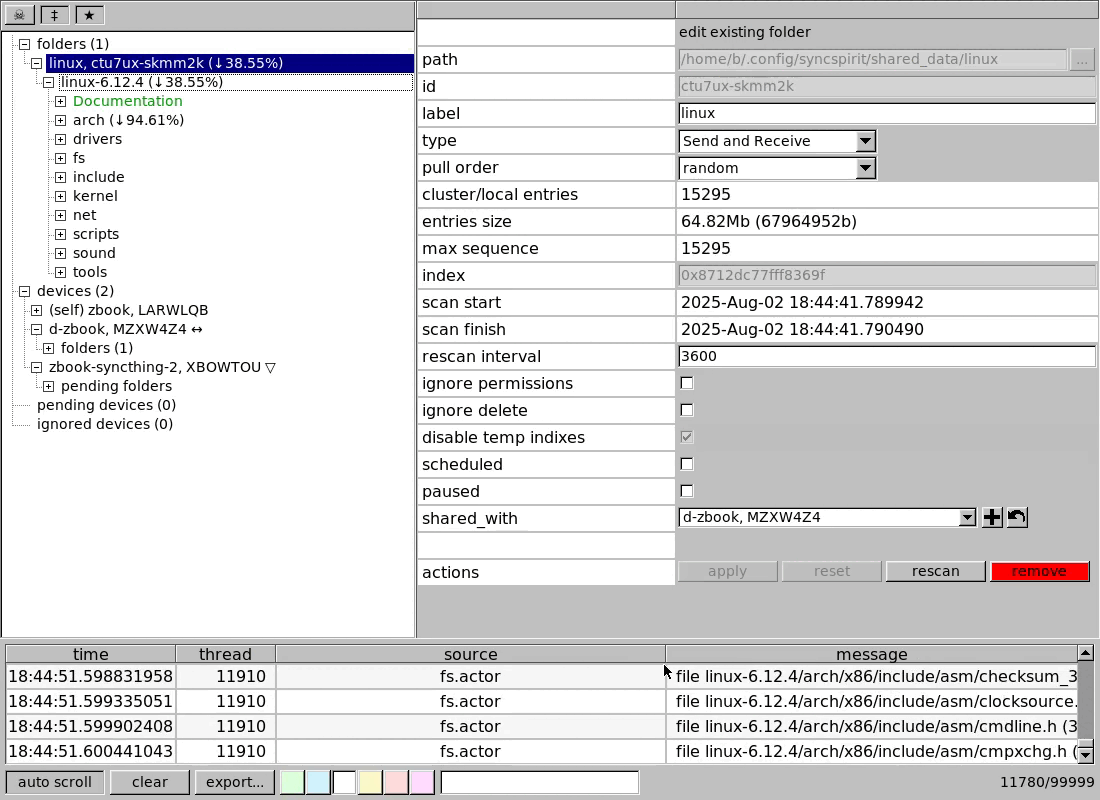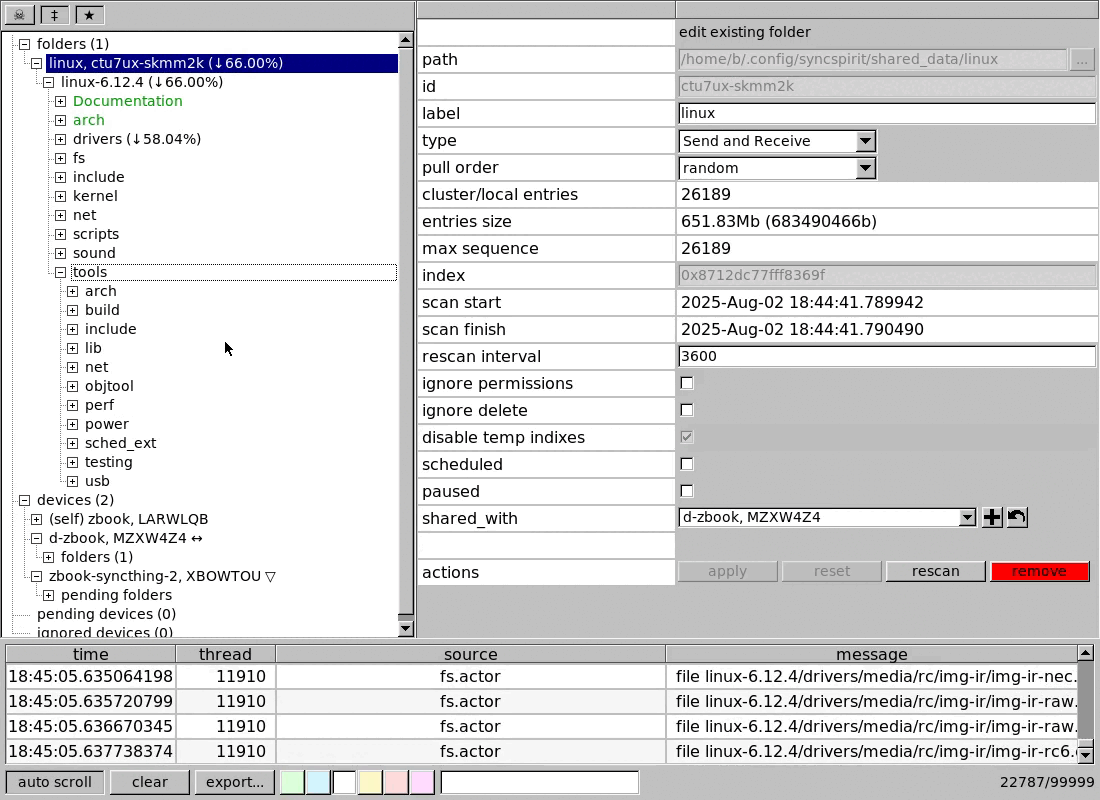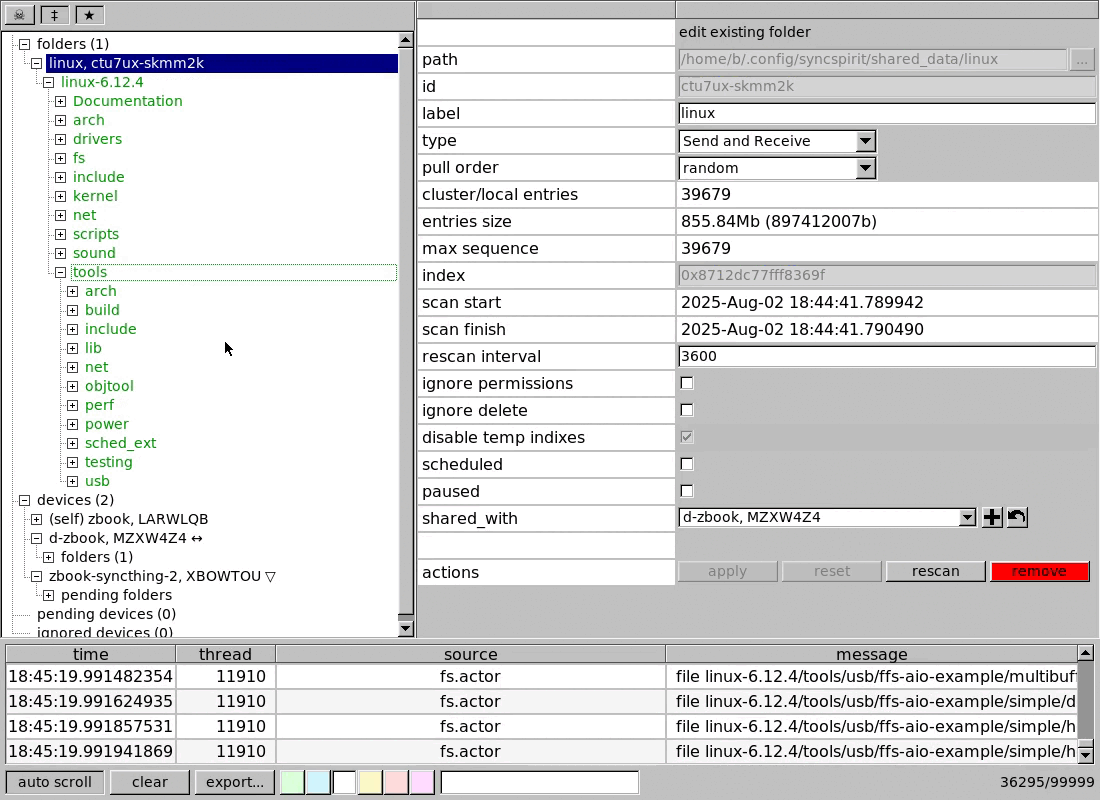


cross-posted from: https://lemmy.ml/post/53284374

I'm glad to announce v0.4.7 release!

Syncspirit is continuous peer-to-peer realtime syncrhonization tool. It implements BEP protocol and provides seamless interoperability with existing syncthing nodes and clients.

https://raw.githubusercontent.com/basiliscos/syncspirit/refs/heads/master/docs/fltk-overview.gif

You can download ready-to-use binaries for Linux x86_64 (AppImage), Windows 32 bit (WindowsXP is supported), Windows 64 bit and Mac OS X (Apple silicon).

Notable changes (since previous v0.4.5 announce):

  • [core, fltk] allow to use file patterns (PCRE-syntax) accept or ignore local files into cluster
  • [core] add start offline option
  • [fltk, win32, os x] add system tray icon
  • [fltk] use menu instead of toolbar
  • [core] introduce services layer (allow stop/start/restart of networking)
  • [core] dns resolver actor: randomly choose ip address of resolver server
  • [core, fix] more reliably connect to relays.syncthing.net
  • [core, win32, bugfix] use utf8 for displaying error messages
  • [core, win32, bugfix] allow to use long file paths (260+ symbols)

Syncspirt source code uses GPLv3 license.

Any feedback is welcome!

WBR, basiliscos.

7


This post is an update of the second part of my Moto server series: https://lemmy.zip/post/72142441

Rumor has it that keeping an 8-year-old phone permanently plugged in with its equally ancient Li-ion battery might not be the greatest idea ever conceived.

Some even claimed that a phone needs a battery to work.

Very negative people.

Anyway, I removed it.

Pettyl did not care.

nginx: UP PHP-FPM: UP MariaDB: UP WordPress: UP cloudflared: UP sshd: UP

The battery is currently sitting next to the phone, contributing absolutely nothing to the project.

Pettyl is now running entirely from USB power, at around 37°C, while continuing to serve the website like this is completely normal.

There is, however, one tiny detail the haters may enjoy:

It can’t boot without the battery.

So the official Pettyl disaster recovery procedure is now:

  1. Insert battery
  2. Boot Pettyl
  3. Connect USB power
  4. Remove battery
  5. Pretend this is enterprise infrastructure

The battery is no longer a battery.

It is the starter motor.

I see no problems with this architecture.

Anyway, Part 3 is going great.

8


I'm curious as to which tools and technologies you all are using to keep track of all those services you are deploying, whether it be resource tracking, network traffic, logs, traces, or uptime.

As a bonus question, how have you organized your network or your services to reduce the overhead of implementing observability?

9


Fine, fine. You asked for it, here it is. I hope you're happy :)

I had to use GPT for the documentation and final spit-and-polish, because I had absolutely no intention of releasing this thing, let alone documenting it for wider consumption.

Ipso facto, for all the AI “Akshually” pedants, I’ve tagged this as AIP. Politely go fuck yourselves :)

Furthermore, here is the actual tale of the tape:

  • Design - HUMAN
  • Implementation - HUMAN
  • Testing - BONE-FUCKING-CRUSHINGLY HUMAN
  • Documentation - GENERATED
  • Review - PAIR

A couple of notes:

  • Remote access: outside the home, the nature of the beast means you need something like Tailscale to get back into your home lab. That’s a quirk I deliberately kept for the sake of simplicity, as the browser needs HTTPS for things like GPS/geolocation. The private Tailscale HTTPS path solves both problems neatly without me having to do shit.

  • Portability: I didn’t build this for you; I built it for me. That said, I detangled the original home-lab-specific mess enough that you should be able to deploy it elsewhere.

The repo separates the application from the regional data bundle, and the documentation covers installation, other regions, routing, Wikipedia/Kiwix, Tailscale, updating and the various caveats.

In other words: it is now usable by other people (and immediately usable if you happen to live where I do), but you'll need to do the work. Additionally, that should not be mistaken for me volunteering to become your unpaid support department :)

"Fork it, fix it or fuck it" - dealers choice :)

10


I'm thinking about buying a Raspberry Pi to start my self-hosted journey. I have three usecases in mind: Navidrome server, Jellyfin server and a Pi-hole network ad-blocking. Can a single machine (like a Raspberry Pi) run these operations simultaneously? Thanks in advance!

11


For a growing number of reasons, as with most people here, I am more desirous of self-hosted solutions to replace proprietary ones, yet, as with many others, I am not in a position to fully self-host with a server at home. Any comments on kinda-self-host, where you rent a server from a third party and do all the same shenanigans on it? Specifically, I'm thinking of data storage and streaming.

Please share any information resources if you can.

12


I usually connect with my server via ssh in a terminal and run basic commands. What's a better, more efficient and modern way of doing that? Especially considering ai and documentation along the way? I wonder if there's a better approach than "connect from remote and act local". Is there a method to "code local and push to remote"?

I use a fedora server with podman, caddyfile and vi.

13


We did it boys! Battery is no more: https://lemmy.zip/post/72181546

This post is a follow-up to my original post: https://lemmy.zip/post/71885626

Surprisingly, it wasn’t that tough to set up.

My original plan was to install postmarketOS and turn the phone into a proper tiny Linux server. Unfortunately, my Moto E5 Play is the pettyl variant, while the available postmarketOS port is for james. I decided that turning the phone into a brick probably wasn’t an essential part of the project.

So I went with Termux instead.

It’s now running nginx, PHP, MariaDB, WordPress, SSH and cloudflared directly on the phone. Everything starts automatically on boot, and I even made a tiny WordPress plugin for anonymous Today / Total / Online visitor stats.

And yes, the website is being served by the exact phone in the photo.

1 GB of RAM. Somehow this thing is now a production server.

I named it Pettyl, after the device codename.

You can actually visit it at https://moto.dimitrium.org/.

The website is barebones, I plan to push it to the limits. Also, this project will soon be available on my GitHub page https://github.com/tradicije

Next problem: figuring out how long an old Motorola can tolerate my bullshit.

14


Why isn't there one service that combines rss reader and bookmarking?
@selfhosted

15
Pi maps: glorious (aussie.zone)
submitted 2 days ago* (last edited 1 day ago) by to c/selfhosted@lemmy.world


TL;DR of the TL;DR: Private, self hosted, GPS enabled, local search and offline routing map engine in under a gigabyte, on a $55 SBC, accessible anywhere.

Ok...I've been working on this for a while and it is SO satisfying to see it to completion.

I'm calling it "Pi maps" (because the Pi hosts it) but it's really MapLibre GL JS, served locally by nginx. The Western Australia basemap is a single PMTiles archive, clipped from the Protomaps daily build to the WA boundary, zoom levels 0-15. The finished stack is about 300 MB.

300MB!

PMTiles is one of the bits I particularly like. Instead of running a tile server and maintaining millions of little tile files or a tile database, nginx just serves one archive with HTTP Range requests. Then MapLibre asks for the byte ranges it needs.

The map-serving path is:

Browser
  ↓
MapLibre GL JS
  ↓
PMTiles JS
  ↓
nginx HTTP Range requests
  ↓
WA.pmtiles

And the best part is that I needed no PostgreSQL, PostGIS or live calls to Google etc.

But wait...there's more! Search and routing!

Rather than install something heavy, I put together a small search service using Python, from the OSM extract.

The source data is converted into a SQLite FTS5 database and the current index contains about 300,000 source records, for a whopping...78 MB. The runtime search service uses about 11 MB RAM at idle.

Driving routes are calculated locally using BRouter, which runs as its own container and nginx proxies the route API internally to it.

The routing dataset for turned out to be remarkably small - roughly 20 MB, with a single worker and a 128 MB Java heap.

The browser gets route geometry, distance, ETA and turn instructions without calling an external routing service.

TL;DR: The current stack is basically three containers:

  • pi-maps - nginx + the MapLibre frontend + PMTiles
  • pi-maps-search - Python + SQLite FTS5 local search
  • pi-maps-brouter - local driving-route engine

After testing, the individual Maps components were around:

nginx/frontend       ~7.3 MiB
search service       ~11.2 MiB
BRouter              ~168 MiB
--------------------------------
total                ~187 MiB RAM

The complete thing - map, search database, routing data, local web assets, metadata etc ends up at roughly 300 MB (excluding the optional ZIM file).

So - a Raspberry Pi 4 is locally serving a zoomable map, POI/address search and actual driving routes for comfortably under a gigabyte of application data.

What's more, I can use it remotely via Tailscale if I want and/or download the tiles directly to my phone and use it with something like GeoLibre or Atlas.

OSM / Protomaps data
        ↓
   Raspberry Pi
        ↓
 ┌───────────────┐
 │ WA.pmtiles    │ → map
 │ SQLite FTS5   │ → search
 │ BRouter       │ → directions
 └───────────────┘
        ↓
 Browser / phone / apps

It's not yet a Google Maps replacement. Yet. Right now the routing profile is driving-focused; there is no live turn-by-turn rerouting, spoken navigation, traffic data, or giant commercial address database. But...I have ideas and too much free time (actually, I think I can solve the 4 of those 5 pretty simply).

Case in point: there was a cool technical problem in that the the POI polygon centroid can be a valid map location but NOT a valid driving destination. That was fun to solve.

The next thing I'm going to try is adding a wikipedia layer - or rather, a self hosted ZIM wikipedia layer - so that POIs actually resolve to clickable entries.

There. For once, I win.

PS: This was much easier to do that the whole "family chat" bullshit. Never work with children or animals.

PPS: Also, I may have broken the family chat IRC server, or at least, misunderstood how IRC uses connection resets. So..XMPP might win after all, much to my chagrin.

EDIT: As requested - https://aussie.zone/post/36966090

16
submitted 2 days ago* (last edited 2 days ago) by to c/selfhosted@lemmy.world


I stumbled upon a post that tells about a project not by the author, and the project has signs of AI. The post is clearly saying the project is good, so I interpreted it as a promotion, but maybe I am wrong. Should that kind of post still be marked as [AIP] ?

The post is https://lemmy.world/post/52316345

17
18


cross-posted from: https://discuss.online/post/45939555

See my post on their forum, which I hope is well received.

19


Hi y'all looking for advice here

I selfhost a nextcloud server and a NAS for backups, and one of my challenges has been data corruption after power failures.

I went and bought some consumer UPS units about 5 years ago, which helped, but now the batteries are starting to fail, and I'm not protected from power outages until I replace them.

I have the router on UPS as well so the computers can communicate with each other that the power has failed and it is time to gracefully shut down (using NUT).

However the router itself uses quite a bit of power and I am hoping to make a smarter decision this time around when getting a UPS.

The router's power supply is 12V5A with a barrel style jack, so i have been searching for "DC UPS 12V 5A" to try and find something compatible that wastes less energy converting from battery DC to AC for the power supply to then convert back to DC.

But the only thing I've been able to find are these units designed to power electric doors: https://www.amazon.com/dp/B0D8VLPRN2/

I'm not sure if this would even be safe to use with a router, and i don't know how i would wire it up to the router either.

I think i just don't have enough knowledge to know how to shop for an appropriate DC UPS, or if such a thing even exists.

Anyone been in a similar situation?

20


Probably old hat to some...but documentation is important. Just for once...I am trying to keep documentation AHEAD of the inevitable bork that destroys everything... so that in 3 months time I don't have to reconstitute everything out of thin air and swearing.

Anyhow, I came across this lovely little repo a while ago and though "yes, next time, use this"

https://github.com/Zavy86/WikiDocs

And so I am :)

I'll let the author speak to the perks (no affiliation, I just like wikidocs and wanted to share it)

  • Open source
  • Plain text files
  • No database required
  • Markdown syntax
  • YAML Frontmatter
  • Editor full WYSIWYG
  • Support for KaTeX math
  • Support for Mermaid diagrams
  • Unlimited page revisions
  • Uploading and downloading attachments
  • Uploading images (also from clipboard)
  • Content can be categorized in namespaces
  • Public and private browsing
  • Desktop and remote sync
  • Syntax highlighting
  • Multiple languages
  • Dark mode

While I show off a happy snap

21
submitted 4 days ago* (last edited 4 days ago) by to c/selfhosted@lemmy.world


tl;dr: Proxmox or bare metal? Containers yes/no? What is your use case?

I used a Dell R710 when I first started self-hosting, it ran ESXi with one VM for each service I wanted. Restarting the server required me to first shutdown each VM in order and then the whole host. When setting up a new service to host I had to create a new VM (allocate RAM, disk etc), install the OS (I ran Debian) and then follow instructions for how to setup the service. This mostly was not a problem but one software I never managed to get working was Apache Guacamole.

Nowadays I have a Dell Optiplex I salvaged for parts, got a new case and all my HDDs from my R710. Because it has much less RAM and an old Intel i5 (6th or 7th generation), I decided to get into Docker. With Docker containers you write your compose file and it will just work. No more need to dig through documentation for which version of a dependency to use, how to handle if two services on the same host need different versions (this was part of the reason for one VM/service). With Docker, I can try out a software in seconds and have it configured to my liking in minutes.

Today I have NixOS (bare metal) and it comes with Podman which uses systemd. Hence restarting my OS (albeit not that often, almost never unless I mess up my config) is a no-brainer because Podman via systemd will manage everything. Adding, stopping or removing containers in general is easy. I have a script running as a service which will stop a container, create a BTRFS subvolume snapshot, start the service again and start borg backup to backup from the snapshot.

For me using Proxmox would just an extra layer of complexity I don't need. I only have one server and I am the only user.

Questions:

  • Do you use Proxmox instead of a bare metal installation?
  • Do you use containers or do you install manually?
  • What is you use case that requires your setup the way it is?
22


Good news, a security issue that was blocking the draft for the new DNS-PERSIST-01 challenge mode for TLS certificates has been resolved, meaning the challenge can resume moving forward.

Some background for those who aren't up to date:

  • TLS challenges are how self-hosters and many other TLS certificate users prove who they are in order to automate cert renewals.
  • The most popular challenge methods are HTTP-01 (which involves having a live web server answering on port 80 somewhere) and DNS-01 (which involves putting a key given by the TLS authority in your DNS zone in a TXT record temporarily).
  • All the current challenges are conducted "live" and require active online participation on the part of the domain owner each time a cert is approaching expiration.
  • The new DNS-PERSIST-01 challenge would let owners keep a proof in their DNS zone indefinitely (or with self-imposed expirations), eliminating the need for those online sessions.
  • DNS-PERSIST-01 was slated to come out in Q2 this year at the latest and all the popular tools (ACME bots, reverse proxies etc.) have been chomping at the bit to implement it.
  • Unfortunately there's been a security snag. Trying to do things the way DNS-01 did (record only the server-provided proof in DNS) would open DNS-PERSIST-01 to middleman attacks, because unlike DNS-01 where the proof is only there temporarily for a few seconds or a few minutes at the most, in this case the proof would be long-term.
  • Hence issue #64, which has been trying to come up with a way to keep only a partial proof in DNS, and combine it with something issued by the server and something issued by the domain owner to make the whole proof, thus rendering the stuff stored in DNS impossible to use for malicious purposes, yet still sufficient for verifying ownership periodically.

Hopefully now that this hurdle has been passed things will proceed faster and we'll get to use this in the near future.

23


cross-posted from: https://lemmy.world/post/52289547

Hey Lemmy, longtime open source developer here. After about a year of work on a side-project I dropped the first release candidate of Plume, a self-hosted, Markdown-powered, flat-file publishing platform and I'd love this community's feedback. Read the release announcement or check out the demo and let me know what you think.

What is Plume?

Plume is a publishing (i.e. blogging) platform. It's designed to make writing and publishing frictionless. Your content is just files, plain Markdown in a flat-file structure without a database. You can write locally and upload via SFTP or keep everything in Git and sync automatically. It's Dockerized out of the box for easy set up. Full-text search (powered by YetiSearch) is built in so there's no external service to wire up. Plume also includes details you'd expect like Shiki syntax highlighting, automatic light and dark modes and an auto-generated RSS feed.

The stack

Plume is written in PHP using Slim Framework + PHP-DI, tested with PHPUnit, statically analyzed with PHPStan, styled with PHP-CS-Fixer. The front end utilizes Alpine.js bundled with Vite. The architecture leans on Directory Lister, a project I've maintained for years.

But why?

I primarily developed Plume for my own use. I occasionally like writing short-form on Bluesky (or previously Twitter) but have been growing tired of handing my content to someone else's platform. And long-form writing came with too much friction, killing my motivation before ever actually getting published. With Plume, publishing is as simple as creating a file and writing.

The AI caveat

Most software ships with heavy AI involvement these days. However, Plume was developed in my spare time over the past year, initially without any AI assistance. I've only recently adopted AI, and only sparingly, mainly for debugging, tests and help with documentation. However, every line committed exists because I put it there with intention. I'm not claiming perfection but I know how and why everything works, which matters for the long-term maintenance of the project.

Feedback wanted

Despite being designed for my own use, Plume was intentionally built so it could be shared. So try it, break it and tell me what's missing. Ideas and questions can be posted on GitHub Discussions or Bluesky. For bugs open a GitHub Issue.

Resources

Plume is fully open sourced on GitHub with full documentation is available at docs.plume.pub.

I'll be hanging out in the comments, so ask me anything.

CBH]

24


cross-posted from: https://lemmy.blahaj.zone/post/48313374

Promotional

Im not affiliated to Fermi/Harmony chat in any way, im just a user who liked it and want to share my experience of the app i find worthy of sharing

so i wanted to share a promising project that I have been using for a few months.

made this post to promote and share this platform since it needs more people, theres arent many atm and it deserves way more.

Fermi/Harmony Chat is free and open source discord like guild/community centered chat platform with most of the features that are expected from those platforms like message channels, vocal chats, threads, screensharing and more. Importantly the chat platform has a strict stance against LLMs AIs and AI generated slop like vibe coding and other abusive usage of AI that replaces human work and slop it in the process. sadly fermi/harmony is unique of having a strong stance against AI. (other similar projects sadly uses AI and excuses AI usage and vibe coding)

the platform also allows users to create their own client for the platform. harmony chat is the API and fermi is just the currently only working client on the platform (was a spacebar client previously until harmony was created as a spacebar fork with the goal of fixing the many issues and bugs present on spacebar) and in the future, instances are going to be federated and the process will be managed directly by the client (fermi and other clients) without being tidious and for advanced users like on matrix, so more easy and beginner friendly.

the platform also is more lenient on its acceptable policy and have a no bullshit moderation. (sadly not the case for other alternatives which sucks very much)

IMPORTANT

currently the project in its early stage and still has lots of bugs, glitches and various issues.

it is currently only accessible through a web browser (there is no app neither on desktop or on mobile)

lots of features are not finished and the platform still need major improvements. but i hope it is going to grow and become a viable alternative.

currently there are around 800 people are registered on fermi/harmony chat.

fermi.chat the main website currently (use this one to register) melodychat.org the organisation's website (its called melody on codeberg and on the website since harmony was taken)

codeberg link of both harmony and fermi :

https://codeberg.org/MelodyChat/Harmony https://codeberg.org/MelodyChat/Fermi

credit to Mathium5, eliza, devs and contributors for developping and maintaining fermi and harmony chat.

25


Recently it's come to my attention that Caddy has an AI sponsor so I have been looking at moving away from Caddy.

I'm currently looking for another reverse proxy to use in place of Caddy. For TLS I am looking into using CertBot and it appears there's a module (https://github.com/desec-io/certbot-dns-desec) I can use that works for https://desec.io/ to handle my certs.

I have two questions, the first is about CertBot. Since Caddy is handling my certs automatically, how often would I want to renew my certs? Desec.io has this command to obtain a cert:

certbot certonly \
     --authenticator dns-desec \
     --dns-desec-credentials /etc/letsencrypt/secrets/$DOMAIN.ini \
     -d "$DOMAIN" \
     -d "*.$DOMAIN"

Would I be required to run the same command periodically to renew my cert?

My second question is a bit more open ended. I am looking to hear any suggestions or experiences about different reverse proxies that are preferably free of AI. There is a list here with some suggested alternatives: https://codeberg.org/ethical-foss/open-slopware#web-servers

view more: next ›