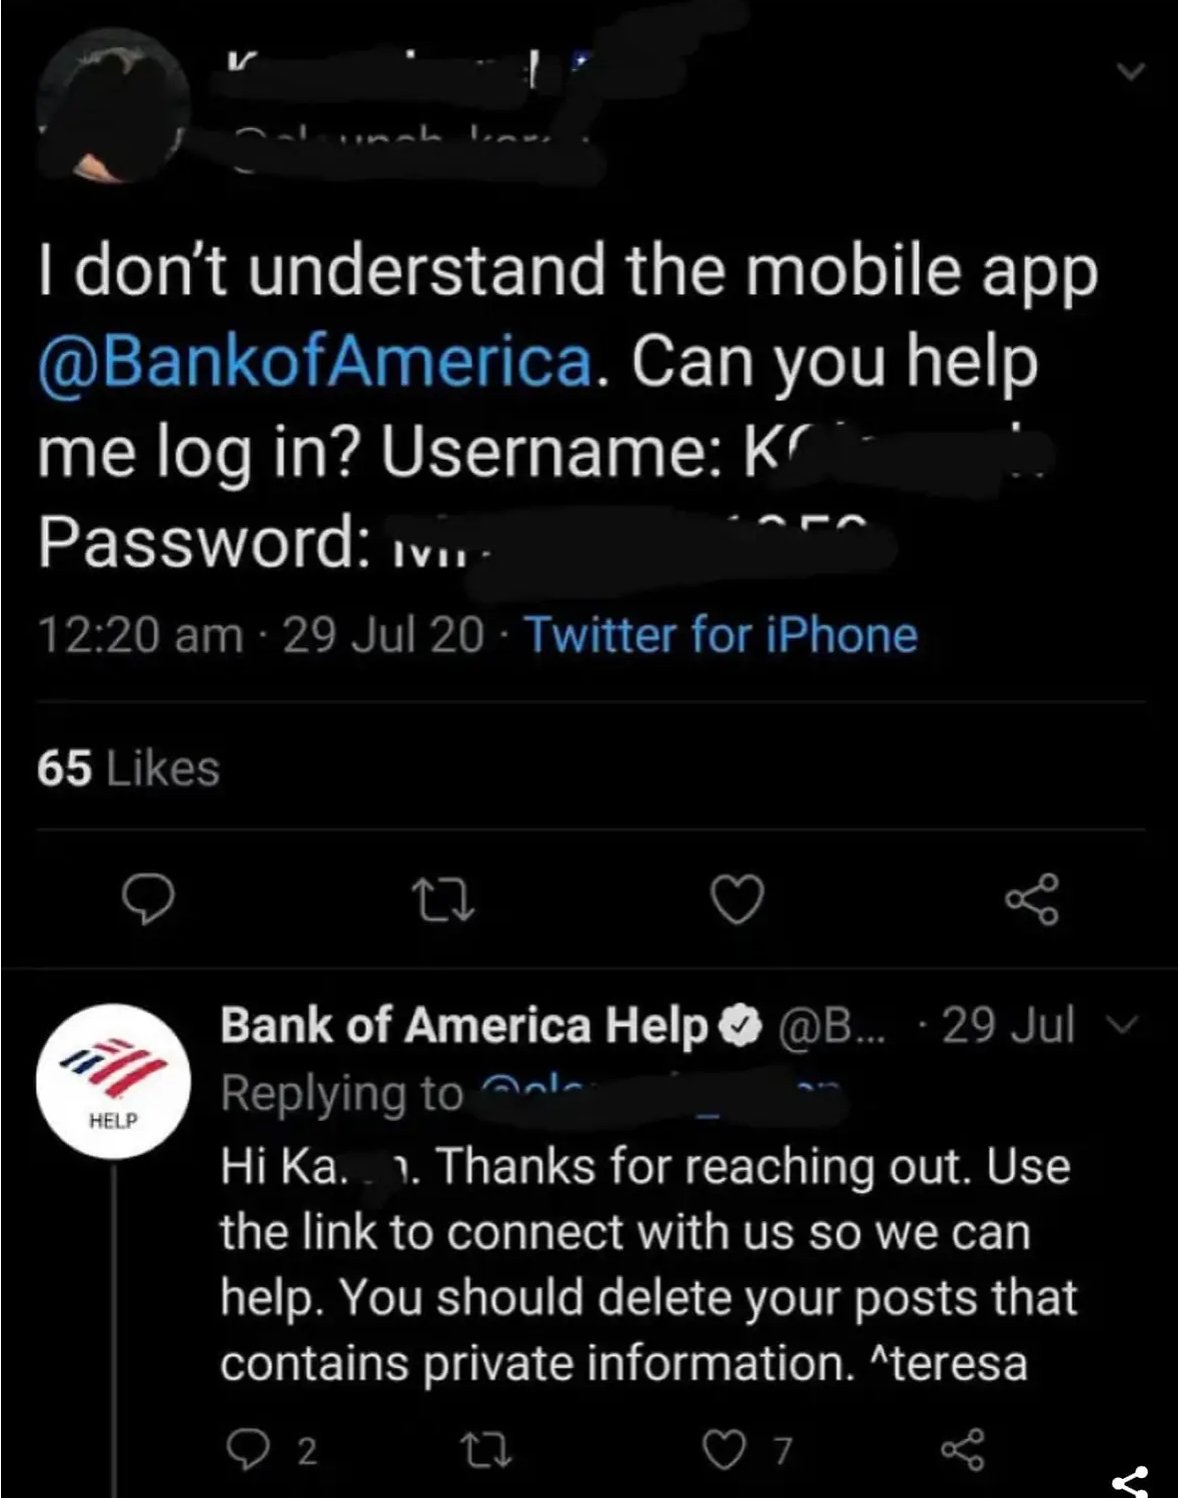
you are viewing a single comment's thread
view the rest of the comments
[–] 134 points 2 years ago (35 children)

Their policy should just be to reset the password immediately and have the user set a new one. This is one hell of a risk.

  • source
  • hideshow 35 child comments
  • [–] 42 points 2 years ago (32 children)

    I still can’t believe American banks lets you login with just username / password? Surely there is some id check or at least two factors involved?

  • source
  • parent
  • hideshow 32 child comments
  • [–] 34 points 2 years ago* (21 children)

    Nope, several years ago someone complained that their steam account has better protection then their bank account. We're now in 2023 and that statement still holds. It's quite scary really. Bank websites that heavily rely on third party scripts ,"MFA" logins based on something you know and something you know. Account verification question based on code words or security questions based on public information. Worst of all, the ignorance of it all. "We got hacked, here have a identity protection bandage, comes with an automatic subscription after several years".

  • source
  • parent
  • hideshow 21 child comments
  • [–] 3 points 2 years ago (9 children)

    I wanted to use a 2FA device for my banking accounts and no bank that I have spoken to would allow it. I'd had a breach on one account because my information had been leaked from several different places including the federal government and a credit agency and as a result the person used my leaked information to validate their way into my checking account. At that point they let me set up a pass phrase and a couple of other random safeguards. This was all well and good but it didn't make me feel safer than having that account protected by a physical 2FA device. I was also given more free credit monitoring (which I've gotten like 4 or 5 times in the last 10 years or so). Still bugs me to this day.

  • source
  • parent
  • hideshow 9 child comments
  • [–] 5 points 2 years ago* (7 children)

    Bank of America has two factor and optional 3 three factor integration, what are you talking about?

    https://www.eff.org/deeplinks/2016/12/how-enable-two-factor-authentication-bank-america

  • source
  • parent
  • hideshow 7 child comments
  • [–] 3 points 2 years ago (6 children)

    Bank of America is not one of the banks I talked to because I will never bank with them again. I was 18 and they sent me (unsolicited) a credit card when I opened my first checking account. It had A 35% interest rate.

  • source
  • parent
  • hideshow 6 child comments
  • [–] 3 points 2 years ago (4 children)

    Commerce, Midwest, citi, and most if not all state banks have 2fa at this point.

  • source
  • parent
  • hideshow 4 child comments
  • [–] 2 points 2 years ago* (last edited 2 years ago) (3 children)

    2fa with a physical key? Also it's been more than a year since I last checked at all.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 3 points 2 years ago* (2 children)

    Via third party integration yes. Outside of that is user/password then they send a code to your email or phone you enter that and it bumps you to third party if you've requested it.

    https://www.bankofamerica.com/security-center/online-mobile-banking-privacy/usb-security-key/

  • source
  • parent
  • hideshow 2 child comments
  • Here's the silly thing - most other countries have had a form of 2FA for decades. Yes, decades. Some of the earliest ones used to sent you a printed list of codes and asked you a random code from that list. This was before the Internet even when you had to use a modem to dial in to a bank to transmit your transactions.

  • source
  • parent
  • [–] 3 points 2 years ago (9 children)

    Yes, they do. Wtf is even happening in this thread.

  • source
  • parent
  • hideshow 9 child comments
  • [–] 1 point 2 years ago (8 children)

    There are some that do, true, but also a boatload that don't. In my personal experience, most don't.

  • source
  • parent
  • hideshow 8 child comments
  • [–] 3 points 2 years ago (7 children)

    Most do, unless they're some small town bank. That could be the difference, perhaps.

  • source
  • parent
  • hideshow 7 child comments
  • [–] 2 points 2 years ago (1 child)

    Most interesting, I checked 2fa.directory and lo and behold, one of them shows that use 2fa! It's the dinky SMS one, but still better then none! Sad part is that a) they never informed me and b) it's completely optional also c) this must be something from the last year or so as I'm one of those people who actively gives feedback

  • source
  • parent
  • hideshow 1 child comment
  • [–] 1 point 2 years ago (4 children)

    Chase is a small town bank? TIL

  • source
  • parent
  • hideshow 4 child comments
  • [–] 1 point 2 years ago (1 child)

    Schwab has 2fa, and isn't Schwab literally owned by Chase? Wtf

  • source
  • parent
  • hideshow 1 child comment
  • [–] 6 points 2 years ago (6 children)

    Yeah I'm European end my job in accounting makes me have to work with American banks regularly. So let's just say my expectations on American banks are quite low.

  • source
  • parent
  • hideshow 6 child comments
  • [–] 1 point 2 years ago (5 children)

    Wait, American banks don't go with extra authentication? I couldn't log in anywhere without SMS or additional apps or whatever. Depending on your bank you might even have to go through three different stages of authentication. Over the pond you just go username / password?

  • source
  • parent
  • hideshow 5 child comments
  • [–] 2 points 2 years ago (4 children)

    They do. It's not as stout as basically anywhere else but 2fa is and has been a thing here for quite some time and specifically as long as I've banked Mobile ACC that's gotta be 5 years+.

    I'm honestly not sure where this whole comment chain is coming from , I guess people don't just ask and instead assume it's not offered. I dunno it's a very weird argument to me since my bank has always had 2fa and alllows third party geolocating 3fa.

  • source
  • parent
  • hideshow 4 child comments
  • [–] 12 points 2 years ago* (last edited 2 years ago)

    That would imply they have to test that the credentials are correct though.

    Otherwise I can just put somebody's user and put some fake password and they would reset it and disconnect the account of that user and annoy him.

  • source
  • parent
  • [–] 7 points 2 years ago

    But the username is still public, you can change the password but if your customer is idiotic enough to blast both out into the internet, the password will just get a 1 or ! After the password they used before...

  • source
  • parent