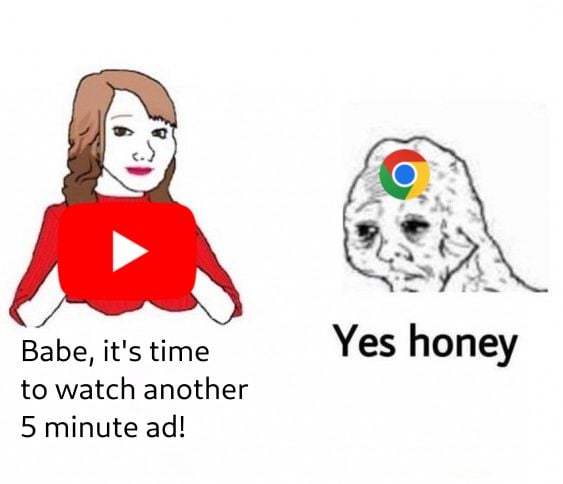
▲ 1202 ▼ You WILL use chrome, and you WILL watch the ads! (lemmy.world) submitted 3 years ago by Spudwart@lemmy.world to c/memes@lemmy.ml 119 comments fedilink hide all child comments
[–] chemicalwonka@discuss.tchncs.de 29 points 3 years ago (13 children) My future browser will be a terminal prompt permalink fedilink source hideshow 13 child comments replies: [–] davidisgreat@lemmy.sedimentarymountains.com 20 points 3 years ago (12 children) You can use Lynx. Here is the google homepage: permalink fedilink source parent hideshow 12 child comments replies: [–] chemicalwonka@discuss.tchncs.de 8 points 3 years ago (9 children) Nice. but Unfortunately WEI will detect the header of the request and block site access even with a terminal browser. The end is near. permalink fedilink source parent hideshow 9 child comments replies: [–] nickwitha_k@lemmy.sdf.org 6 points 3 years ago That's when we fork the protocol to remove the garbage. permalink fedilink source parent [–] wanderingmagus@lemm.ee 5 points 3 years ago SearXNG+Peertube/Odyssee+Mastodon+Lemmy/kbin+Radarr++nyaa.si+sonarr+ProtonMail+Krita+Monkrus Arr me hearties. permalink fedilink source parent [–] lntl@lemmy.ml 4 points 3 years ago (4 children) Spoof the header? permalink fedilink source parent hideshow 4 child comments replies: [–] chemicalwonka@discuss.tchncs.de 5 points 3 years ago* (last edited 3 years ago) (3 children) WEI will request a authentication token that will be provided by a third part software like Play Store in Android to certificate that your request is made by you a human and not by a bot so technically spoof the header agent will not be effective. Dark times awaits us my friend. Other problem is how deep embedded in the system this trust agent that provides these tokens will be. It may be embedded in kernel like Easy Anti Cheat for example and this will make the things even worse because they can classify many devices like " not approved " just by not meet software or hardware requirements permalink fedilink source parent hideshow 3 child comments replies: [–] lntl@lemmy.ml 0 points 3 years ago (2 children) Compile a kernel? permalink fedilink source parent hideshow 2 child comments replies: [–] chemicalwonka@discuss.tchncs.de 1 point 3 years ago* (1 child) It's no so simple, man. The vast majority of users don't have the skills to do this and I think even if you compile the kernel of your personalized system it will not circumvent WEI and it will brake some functionality somehow permalink fedilink source parent hideshow 1 child comment replies: [–] lntl@lemmy.ml 0 points 3 years ago Develop an API which spoofs authorization authentication tokens? Like man in the middle? permalink fedilink source parent [–] tool@lemmy.world 4 points 3 years ago Changing request headers is a trivial thing. permalink fedilink source parent [–] m3t00@lemmy.world 1 point 3 years ago https://www.searchenginejournal.com/change-user-agent/368448/ permalink fedilink source parent [–] salient_one@lemmy.villa-straylight.social 4 points 3 years ago* Browsh is pretty cool for a text-based browser. permalink fedilink source parent [–] AlittleTooClose@lemmy.blahaj.zone 3 points 3 years ago that's pretty cool! permalink fedilink source parent
[–] davidisgreat@lemmy.sedimentarymountains.com 20 points 3 years ago (12 children) You can use Lynx. Here is the google homepage: permalink fedilink source parent hideshow 12 child comments replies: [–] chemicalwonka@discuss.tchncs.de 8 points 3 years ago (9 children) Nice. but Unfortunately WEI will detect the header of the request and block site access even with a terminal browser. The end is near. permalink fedilink source parent hideshow 9 child comments replies: [–] nickwitha_k@lemmy.sdf.org 6 points 3 years ago That's when we fork the protocol to remove the garbage. permalink fedilink source parent [–] wanderingmagus@lemm.ee 5 points 3 years ago SearXNG+Peertube/Odyssee+Mastodon+Lemmy/kbin+Radarr++nyaa.si+sonarr+ProtonMail+Krita+Monkrus Arr me hearties. permalink fedilink source parent [–] lntl@lemmy.ml 4 points 3 years ago (4 children) Spoof the header? permalink fedilink source parent hideshow 4 child comments replies: [–] chemicalwonka@discuss.tchncs.de 5 points 3 years ago* (last edited 3 years ago) (3 children) WEI will request a authentication token that will be provided by a third part software like Play Store in Android to certificate that your request is made by you a human and not by a bot so technically spoof the header agent will not be effective. Dark times awaits us my friend. Other problem is how deep embedded in the system this trust agent that provides these tokens will be. It may be embedded in kernel like Easy Anti Cheat for example and this will make the things even worse because they can classify many devices like " not approved " just by not meet software or hardware requirements permalink fedilink source parent hideshow 3 child comments replies: [–] lntl@lemmy.ml 0 points 3 years ago (2 children) Compile a kernel? permalink fedilink source parent hideshow 2 child comments replies: [–] chemicalwonka@discuss.tchncs.de 1 point 3 years ago* (1 child) It's no so simple, man. The vast majority of users don't have the skills to do this and I think even if you compile the kernel of your personalized system it will not circumvent WEI and it will brake some functionality somehow permalink fedilink source parent hideshow 1 child comment replies: [–] lntl@lemmy.ml 0 points 3 years ago Develop an API which spoofs authorization authentication tokens? Like man in the middle? permalink fedilink source parent [–] tool@lemmy.world 4 points 3 years ago Changing request headers is a trivial thing. permalink fedilink source parent [–] m3t00@lemmy.world 1 point 3 years ago https://www.searchenginejournal.com/change-user-agent/368448/ permalink fedilink source parent [–] salient_one@lemmy.villa-straylight.social 4 points 3 years ago* Browsh is pretty cool for a text-based browser. permalink fedilink source parent [–] AlittleTooClose@lemmy.blahaj.zone 3 points 3 years ago that's pretty cool! permalink fedilink source parent
[–] chemicalwonka@discuss.tchncs.de 8 points 3 years ago (9 children) Nice. but Unfortunately WEI will detect the header of the request and block site access even with a terminal browser. The end is near. permalink fedilink source parent hideshow 9 child comments replies: [–] nickwitha_k@lemmy.sdf.org 6 points 3 years ago That's when we fork the protocol to remove the garbage. permalink fedilink source parent [–] wanderingmagus@lemm.ee 5 points 3 years ago SearXNG+Peertube/Odyssee+Mastodon+Lemmy/kbin+Radarr++nyaa.si+sonarr+ProtonMail+Krita+Monkrus Arr me hearties. permalink fedilink source parent [–] lntl@lemmy.ml 4 points 3 years ago (4 children) Spoof the header? permalink fedilink source parent hideshow 4 child comments replies: [–] chemicalwonka@discuss.tchncs.de 5 points 3 years ago* (last edited 3 years ago) (3 children) WEI will request a authentication token that will be provided by a third part software like Play Store in Android to certificate that your request is made by you a human and not by a bot so technically spoof the header agent will not be effective. Dark times awaits us my friend. Other problem is how deep embedded in the system this trust agent that provides these tokens will be. It may be embedded in kernel like Easy Anti Cheat for example and this will make the things even worse because they can classify many devices like " not approved " just by not meet software or hardware requirements permalink fedilink source parent hideshow 3 child comments replies: [–] lntl@lemmy.ml 0 points 3 years ago (2 children) Compile a kernel? permalink fedilink source parent hideshow 2 child comments replies: [–] chemicalwonka@discuss.tchncs.de 1 point 3 years ago* (1 child) It's no so simple, man. The vast majority of users don't have the skills to do this and I think even if you compile the kernel of your personalized system it will not circumvent WEI and it will brake some functionality somehow permalink fedilink source parent hideshow 1 child comment replies: [–] lntl@lemmy.ml 0 points 3 years ago Develop an API which spoofs authorization authentication tokens? Like man in the middle? permalink fedilink source parent [–] tool@lemmy.world 4 points 3 years ago Changing request headers is a trivial thing. permalink fedilink source parent [–] m3t00@lemmy.world 1 point 3 years ago https://www.searchenginejournal.com/change-user-agent/368448/ permalink fedilink source parent
[–] nickwitha_k@lemmy.sdf.org 6 points 3 years ago That's when we fork the protocol to remove the garbage. permalink fedilink source parent
[–] wanderingmagus@lemm.ee 5 points 3 years ago SearXNG+Peertube/Odyssee+Mastodon+Lemmy/kbin+Radarr++nyaa.si+sonarr+ProtonMail+Krita+Monkrus Arr me hearties. permalink fedilink source parent
[–] lntl@lemmy.ml 4 points 3 years ago (4 children) Spoof the header? permalink fedilink source parent hideshow 4 child comments replies: [–] chemicalwonka@discuss.tchncs.de 5 points 3 years ago* (last edited 3 years ago) (3 children) WEI will request a authentication token that will be provided by a third part software like Play Store in Android to certificate that your request is made by you a human and not by a bot so technically spoof the header agent will not be effective. Dark times awaits us my friend. Other problem is how deep embedded in the system this trust agent that provides these tokens will be. It may be embedded in kernel like Easy Anti Cheat for example and this will make the things even worse because they can classify many devices like " not approved " just by not meet software or hardware requirements permalink fedilink source parent hideshow 3 child comments replies: [–] lntl@lemmy.ml 0 points 3 years ago (2 children) Compile a kernel? permalink fedilink source parent hideshow 2 child comments replies: [–] chemicalwonka@discuss.tchncs.de 1 point 3 years ago* (1 child) It's no so simple, man. The vast majority of users don't have the skills to do this and I think even if you compile the kernel of your personalized system it will not circumvent WEI and it will brake some functionality somehow permalink fedilink source parent hideshow 1 child comment replies: [–] lntl@lemmy.ml 0 points 3 years ago Develop an API which spoofs authorization authentication tokens? Like man in the middle? permalink fedilink source parent
[–] chemicalwonka@discuss.tchncs.de 5 points 3 years ago* (last edited 3 years ago) (3 children) WEI will request a authentication token that will be provided by a third part software like Play Store in Android to certificate that your request is made by you a human and not by a bot so technically spoof the header agent will not be effective. Dark times awaits us my friend. Other problem is how deep embedded in the system this trust agent that provides these tokens will be. It may be embedded in kernel like Easy Anti Cheat for example and this will make the things even worse because they can classify many devices like " not approved " just by not meet software or hardware requirements permalink fedilink source parent hideshow 3 child comments replies: [–] lntl@lemmy.ml 0 points 3 years ago (2 children) Compile a kernel? permalink fedilink source parent hideshow 2 child comments replies: [–] chemicalwonka@discuss.tchncs.de 1 point 3 years ago* (1 child) It's no so simple, man. The vast majority of users don't have the skills to do this and I think even if you compile the kernel of your personalized system it will not circumvent WEI and it will brake some functionality somehow permalink fedilink source parent hideshow 1 child comment replies: [–] lntl@lemmy.ml 0 points 3 years ago Develop an API which spoofs authorization authentication tokens? Like man in the middle? permalink fedilink source parent
[–] lntl@lemmy.ml 0 points 3 years ago (2 children) Compile a kernel? permalink fedilink source parent hideshow 2 child comments replies: [–] chemicalwonka@discuss.tchncs.de 1 point 3 years ago* (1 child) It's no so simple, man. The vast majority of users don't have the skills to do this and I think even if you compile the kernel of your personalized system it will not circumvent WEI and it will brake some functionality somehow permalink fedilink source parent hideshow 1 child comment replies: [–] lntl@lemmy.ml 0 points 3 years ago Develop an API which spoofs authorization authentication tokens? Like man in the middle? permalink fedilink source parent
[–] chemicalwonka@discuss.tchncs.de 1 point 3 years ago* (1 child) It's no so simple, man. The vast majority of users don't have the skills to do this and I think even if you compile the kernel of your personalized system it will not circumvent WEI and it will brake some functionality somehow permalink fedilink source parent hideshow 1 child comment replies: [–] lntl@lemmy.ml 0 points 3 years ago Develop an API which spoofs authorization authentication tokens? Like man in the middle? permalink fedilink source parent
[–] lntl@lemmy.ml 0 points 3 years ago Develop an API which spoofs authorization authentication tokens? Like man in the middle? permalink fedilink source parent
[–] tool@lemmy.world 4 points 3 years ago Changing request headers is a trivial thing. permalink fedilink source parent
[–] m3t00@lemmy.world 1 point 3 years ago https://www.searchenginejournal.com/change-user-agent/368448/ permalink fedilink source parent
[–] salient_one@lemmy.villa-straylight.social 4 points 3 years ago* Browsh is pretty cool for a text-based browser. permalink fedilink source parent
[–] AlittleTooClose@lemmy.blahaj.zone 3 points 3 years ago that's pretty cool! permalink fedilink source parent