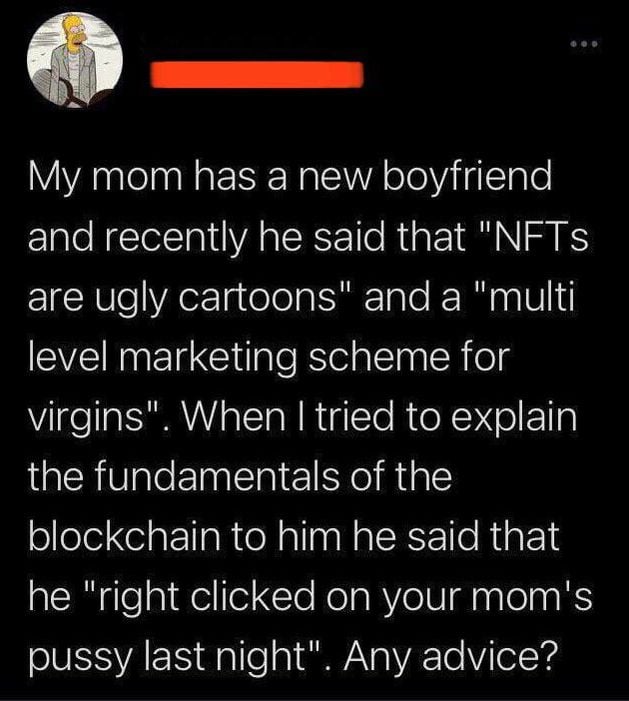
▲ 974 ▼ None. Suffer. (lemmy.world) submitted 2 years ago by Stamets@lemmy.world to c/whitepeopletwitter@sh.itjust.works 159 comments fedilink hide all child comments
[–] magnetosphere@fedia.io 2 points 2 years ago (16 children) Interesting. Good to know. Thanks! permalink fedilink source parent hideshow 16 child comments replies: [–] Serinus@lemmy.world 24 points 2 years ago Blockchain is effectively a distributed database. Almost always a good centralized database functions better. permalink fedilink source parent [+] simplymath@lemmy.world -7 points 2 years ago* (14 children) Nah. the commenter above is just wrong. It's just that anyone who isn't selling bullshit uses their real name- Merkel trees - which are fundamental to modern software development (git, zfs, nix, nosql). permalink fedilink source parent hideshow 14 child comments replies: [–] ryathal@sh.itjust.works 11 points 2 years ago (12 children) That's a similar but different concept. Blockchain adds a way to determine consensus of the correct tree. While git is distributed, it's generally not trustless, there's generally a trusted version of the repository. permalink fedilink source parent hideshow 12 child comments replies: [–] simplymath@lemmy.world -5 points 2 years ago* (last edited 2 years ago) (11 children) what? Git is very much distributed and while you can have a main branch, you can set as many up streams as you want and merge things sideways. It's trust less in the sense that commits can't be easily forged and are signed with cryptographic keys and identities-- as in, I don't have to trust that the source code is genuine since I can verify the commit history myself. Consensus is just a pull request. That wiki article literally lists Bitcoin and Ethereum as implementations of Merkel trees. permalink fedilink source parent hideshow 11 child comments replies: [–] ICastFist@programming.dev 3 points 2 years ago (10 children) It’s trust less in the sense that commits can’t be easily forged and are signed with cryptographic keys and identities. I'm pretty sure being able to verify that the person responsible for a push is an actual maintainer is the opposite of trustless. permalink fedilink source parent hideshow 10 child comments replies: [–] simplymath@lemmy.world 2 points 2 years ago* (last edited 2 years ago) (9 children) How is it any different than verifying that a transaction occurred? How is a trusted repository different from a hard fork? Isn't "proving someone is a maintainer" just an IRL proof of stake? permalink fedilink source parent hideshow 9 child comments replies: [–] ICastFist@programming.dev 3 points 2 years ago (8 children) How is it any different than verifying that a transaction occurred? With a centralized trust source (bank), you ask for the records. How is a trusted repository different from a hard fork? Because you check who owns and maintains it. A notable example was with Simple Apps for Android, earlier this year the main repo was sold to a company. Trust was lost, thus a fork was created to keep the original stuff. permalink fedilink source parent hideshow 8 child comments replies: [–] simplymath@lemmy.world 2 points 2 years ago (7 children) Right, but isn't the "main chain" of Ethereum based on a similar principle wherein it's the main chain because it's the one the devs use? What about BTC vs BTC lightning. I'm genuinely failing to see a distinction here, and, again, the wiki article says that blockchains are special cases of Merkle trees. permalink fedilink source parent hideshow 7 child comments replies: [–] ICastFist@programming.dev 2 points 2 years ago (6 children) Right, but isn’t the “main chain” of Ethereum based on a similar principle wherein it’s the main chain because it’s the one the devs use? No clue, I don't keep an eye on that, I'm partially aware that there are several similar forks (and eth classic was a result of scammy shenanigans) but, afaict, none try to pretend they're the "real" ethereum. I’m genuinely failing to see a distinction here A distinction between trust and trustless? Because my initial point was that git isn't trustless, because it works just like any other online system that requires a login, where a central server/database checks if the user sending inputs was properly identified by some mean (password, cryptographic key, something else). Implementing a Merkle or any other hash tree doesn't make something trustless permalink fedilink source parent hideshow 6 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago (5 children) does git require authentication with a central server? I know that's common practice and true of github, but my recollection was that it was meant to fix the problem of distributed kernel development via an email listserv in the early 2000s. This stack exchange post discusses how it's not really centralized permalink fedilink source parent hideshow 5 child comments replies: [–] ICastFist@programming.dev 1 point 2 years ago (4 children) Not being centralized has nothing to do with being trustless. The fediverse is also decentralized, yet you, me and everyone else has to log in to a specific server. If I try to login via lemmy.world, it'll fail. I have to login via programming.dev. Does that make lemmy and the fediverse trustless? No. Even the top answer on that SO question explains that the use case of hash trees for git is different from that of blockchain permalink fedilink source parent hideshow 4 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago (3 children) yeah, but this SO post has many up voted comments supporting my points as well. permalink fedilink source parent hideshow 3 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago 183 votes for your "similar but not the same" and 103 votes for "they are the same". At the very least, I'd say this is far from settled fact permalink fedilink source parent [–] ICastFist@programming.dev 1 point 2 years ago (1 child) You're completely ignoring the point that being decentralized and/or implementing hash trees does not make a system trustless permalink fedilink source parent hideshow 1 child comment replies: [–] simplymath@lemmy.world 2 points 2 years ago no, no. I'm conceding that-- not ignoring that. permalink fedilink source parent [–] simplymath@lemmy.world 1 point 2 years ago We define "blockchain" and "blockchain network", and then discuss two very different, well known classes of blockchain networks: cryptocurrencies and Git repositories. https://arxiv.org/abs/1803.00892 permalink fedilink source parent
[–] Serinus@lemmy.world 24 points 2 years ago Blockchain is effectively a distributed database. Almost always a good centralized database functions better. permalink fedilink source parent
[+] simplymath@lemmy.world -7 points 2 years ago* (14 children) Nah. the commenter above is just wrong. It's just that anyone who isn't selling bullshit uses their real name- Merkel trees - which are fundamental to modern software development (git, zfs, nix, nosql). permalink fedilink source parent hideshow 14 child comments replies: [–] ryathal@sh.itjust.works 11 points 2 years ago (12 children) That's a similar but different concept. Blockchain adds a way to determine consensus of the correct tree. While git is distributed, it's generally not trustless, there's generally a trusted version of the repository. permalink fedilink source parent hideshow 12 child comments replies: [–] simplymath@lemmy.world -5 points 2 years ago* (last edited 2 years ago) (11 children) what? Git is very much distributed and while you can have a main branch, you can set as many up streams as you want and merge things sideways. It's trust less in the sense that commits can't be easily forged and are signed with cryptographic keys and identities-- as in, I don't have to trust that the source code is genuine since I can verify the commit history myself. Consensus is just a pull request. That wiki article literally lists Bitcoin and Ethereum as implementations of Merkel trees. permalink fedilink source parent hideshow 11 child comments replies: [–] ICastFist@programming.dev 3 points 2 years ago (10 children) It’s trust less in the sense that commits can’t be easily forged and are signed with cryptographic keys and identities. I'm pretty sure being able to verify that the person responsible for a push is an actual maintainer is the opposite of trustless. permalink fedilink source parent hideshow 10 child comments replies: [–] simplymath@lemmy.world 2 points 2 years ago* (last edited 2 years ago) (9 children) How is it any different than verifying that a transaction occurred? How is a trusted repository different from a hard fork? Isn't "proving someone is a maintainer" just an IRL proof of stake? permalink fedilink source parent hideshow 9 child comments replies: [–] ICastFist@programming.dev 3 points 2 years ago (8 children) How is it any different than verifying that a transaction occurred? With a centralized trust source (bank), you ask for the records. How is a trusted repository different from a hard fork? Because you check who owns and maintains it. A notable example was with Simple Apps for Android, earlier this year the main repo was sold to a company. Trust was lost, thus a fork was created to keep the original stuff. permalink fedilink source parent hideshow 8 child comments replies: [–] simplymath@lemmy.world 2 points 2 years ago (7 children) Right, but isn't the "main chain" of Ethereum based on a similar principle wherein it's the main chain because it's the one the devs use? What about BTC vs BTC lightning. I'm genuinely failing to see a distinction here, and, again, the wiki article says that blockchains are special cases of Merkle trees. permalink fedilink source parent hideshow 7 child comments replies: [–] ICastFist@programming.dev 2 points 2 years ago (6 children) Right, but isn’t the “main chain” of Ethereum based on a similar principle wherein it’s the main chain because it’s the one the devs use? No clue, I don't keep an eye on that, I'm partially aware that there are several similar forks (and eth classic was a result of scammy shenanigans) but, afaict, none try to pretend they're the "real" ethereum. I’m genuinely failing to see a distinction here A distinction between trust and trustless? Because my initial point was that git isn't trustless, because it works just like any other online system that requires a login, where a central server/database checks if the user sending inputs was properly identified by some mean (password, cryptographic key, something else). Implementing a Merkle or any other hash tree doesn't make something trustless permalink fedilink source parent hideshow 6 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago (5 children) does git require authentication with a central server? I know that's common practice and true of github, but my recollection was that it was meant to fix the problem of distributed kernel development via an email listserv in the early 2000s. This stack exchange post discusses how it's not really centralized permalink fedilink source parent hideshow 5 child comments replies: [–] ICastFist@programming.dev 1 point 2 years ago (4 children) Not being centralized has nothing to do with being trustless. The fediverse is also decentralized, yet you, me and everyone else has to log in to a specific server. If I try to login via lemmy.world, it'll fail. I have to login via programming.dev. Does that make lemmy and the fediverse trustless? No. Even the top answer on that SO question explains that the use case of hash trees for git is different from that of blockchain permalink fedilink source parent hideshow 4 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago (3 children) yeah, but this SO post has many up voted comments supporting my points as well. permalink fedilink source parent hideshow 3 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago 183 votes for your "similar but not the same" and 103 votes for "they are the same". At the very least, I'd say this is far from settled fact permalink fedilink source parent [–] ICastFist@programming.dev 1 point 2 years ago (1 child) You're completely ignoring the point that being decentralized and/or implementing hash trees does not make a system trustless permalink fedilink source parent hideshow 1 child comment replies: [–] simplymath@lemmy.world 2 points 2 years ago no, no. I'm conceding that-- not ignoring that. permalink fedilink source parent [–] simplymath@lemmy.world 1 point 2 years ago We define "blockchain" and "blockchain network", and then discuss two very different, well known classes of blockchain networks: cryptocurrencies and Git repositories. https://arxiv.org/abs/1803.00892 permalink fedilink source parent
[–] ryathal@sh.itjust.works 11 points 2 years ago (12 children) That's a similar but different concept. Blockchain adds a way to determine consensus of the correct tree. While git is distributed, it's generally not trustless, there's generally a trusted version of the repository. permalink fedilink source parent hideshow 12 child comments replies: [–] simplymath@lemmy.world -5 points 2 years ago* (last edited 2 years ago) (11 children) what? Git is very much distributed and while you can have a main branch, you can set as many up streams as you want and merge things sideways. It's trust less in the sense that commits can't be easily forged and are signed with cryptographic keys and identities-- as in, I don't have to trust that the source code is genuine since I can verify the commit history myself. Consensus is just a pull request. That wiki article literally lists Bitcoin and Ethereum as implementations of Merkel trees. permalink fedilink source parent hideshow 11 child comments replies: [–] ICastFist@programming.dev 3 points 2 years ago (10 children) It’s trust less in the sense that commits can’t be easily forged and are signed with cryptographic keys and identities. I'm pretty sure being able to verify that the person responsible for a push is an actual maintainer is the opposite of trustless. permalink fedilink source parent hideshow 10 child comments replies: [–] simplymath@lemmy.world 2 points 2 years ago* (last edited 2 years ago) (9 children) How is it any different than verifying that a transaction occurred? How is a trusted repository different from a hard fork? Isn't "proving someone is a maintainer" just an IRL proof of stake? permalink fedilink source parent hideshow 9 child comments replies: [–] ICastFist@programming.dev 3 points 2 years ago (8 children) How is it any different than verifying that a transaction occurred? With a centralized trust source (bank), you ask for the records. How is a trusted repository different from a hard fork? Because you check who owns and maintains it. A notable example was with Simple Apps for Android, earlier this year the main repo was sold to a company. Trust was lost, thus a fork was created to keep the original stuff. permalink fedilink source parent hideshow 8 child comments replies: [–] simplymath@lemmy.world 2 points 2 years ago (7 children) Right, but isn't the "main chain" of Ethereum based on a similar principle wherein it's the main chain because it's the one the devs use? What about BTC vs BTC lightning. I'm genuinely failing to see a distinction here, and, again, the wiki article says that blockchains are special cases of Merkle trees. permalink fedilink source parent hideshow 7 child comments replies: [–] ICastFist@programming.dev 2 points 2 years ago (6 children) Right, but isn’t the “main chain” of Ethereum based on a similar principle wherein it’s the main chain because it’s the one the devs use? No clue, I don't keep an eye on that, I'm partially aware that there are several similar forks (and eth classic was a result of scammy shenanigans) but, afaict, none try to pretend they're the "real" ethereum. I’m genuinely failing to see a distinction here A distinction between trust and trustless? Because my initial point was that git isn't trustless, because it works just like any other online system that requires a login, where a central server/database checks if the user sending inputs was properly identified by some mean (password, cryptographic key, something else). Implementing a Merkle or any other hash tree doesn't make something trustless permalink fedilink source parent hideshow 6 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago (5 children) does git require authentication with a central server? I know that's common practice and true of github, but my recollection was that it was meant to fix the problem of distributed kernel development via an email listserv in the early 2000s. This stack exchange post discusses how it's not really centralized permalink fedilink source parent hideshow 5 child comments replies: [–] ICastFist@programming.dev 1 point 2 years ago (4 children) Not being centralized has nothing to do with being trustless. The fediverse is also decentralized, yet you, me and everyone else has to log in to a specific server. If I try to login via lemmy.world, it'll fail. I have to login via programming.dev. Does that make lemmy and the fediverse trustless? No. Even the top answer on that SO question explains that the use case of hash trees for git is different from that of blockchain permalink fedilink source parent hideshow 4 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago (3 children) yeah, but this SO post has many up voted comments supporting my points as well. permalink fedilink source parent hideshow 3 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago 183 votes for your "similar but not the same" and 103 votes for "they are the same". At the very least, I'd say this is far from settled fact permalink fedilink source parent [–] ICastFist@programming.dev 1 point 2 years ago (1 child) You're completely ignoring the point that being decentralized and/or implementing hash trees does not make a system trustless permalink fedilink source parent hideshow 1 child comment replies: [–] simplymath@lemmy.world 2 points 2 years ago no, no. I'm conceding that-- not ignoring that. permalink fedilink source parent
[–] simplymath@lemmy.world -5 points 2 years ago* (last edited 2 years ago) (11 children) what? Git is very much distributed and while you can have a main branch, you can set as many up streams as you want and merge things sideways. It's trust less in the sense that commits can't be easily forged and are signed with cryptographic keys and identities-- as in, I don't have to trust that the source code is genuine since I can verify the commit history myself. Consensus is just a pull request. That wiki article literally lists Bitcoin and Ethereum as implementations of Merkel trees. permalink fedilink source parent hideshow 11 child comments replies: [–] ICastFist@programming.dev 3 points 2 years ago (10 children) It’s trust less in the sense that commits can’t be easily forged and are signed with cryptographic keys and identities. I'm pretty sure being able to verify that the person responsible for a push is an actual maintainer is the opposite of trustless. permalink fedilink source parent hideshow 10 child comments replies: [–] simplymath@lemmy.world 2 points 2 years ago* (last edited 2 years ago) (9 children) How is it any different than verifying that a transaction occurred? How is a trusted repository different from a hard fork? Isn't "proving someone is a maintainer" just an IRL proof of stake? permalink fedilink source parent hideshow 9 child comments replies: [–] ICastFist@programming.dev 3 points 2 years ago (8 children) How is it any different than verifying that a transaction occurred? With a centralized trust source (bank), you ask for the records. How is a trusted repository different from a hard fork? Because you check who owns and maintains it. A notable example was with Simple Apps for Android, earlier this year the main repo was sold to a company. Trust was lost, thus a fork was created to keep the original stuff. permalink fedilink source parent hideshow 8 child comments replies: [–] simplymath@lemmy.world 2 points 2 years ago (7 children) Right, but isn't the "main chain" of Ethereum based on a similar principle wherein it's the main chain because it's the one the devs use? What about BTC vs BTC lightning. I'm genuinely failing to see a distinction here, and, again, the wiki article says that blockchains are special cases of Merkle trees. permalink fedilink source parent hideshow 7 child comments replies: [–] ICastFist@programming.dev 2 points 2 years ago (6 children) Right, but isn’t the “main chain” of Ethereum based on a similar principle wherein it’s the main chain because it’s the one the devs use? No clue, I don't keep an eye on that, I'm partially aware that there are several similar forks (and eth classic was a result of scammy shenanigans) but, afaict, none try to pretend they're the "real" ethereum. I’m genuinely failing to see a distinction here A distinction between trust and trustless? Because my initial point was that git isn't trustless, because it works just like any other online system that requires a login, where a central server/database checks if the user sending inputs was properly identified by some mean (password, cryptographic key, something else). Implementing a Merkle or any other hash tree doesn't make something trustless permalink fedilink source parent hideshow 6 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago (5 children) does git require authentication with a central server? I know that's common practice and true of github, but my recollection was that it was meant to fix the problem of distributed kernel development via an email listserv in the early 2000s. This stack exchange post discusses how it's not really centralized permalink fedilink source parent hideshow 5 child comments replies: [–] ICastFist@programming.dev 1 point 2 years ago (4 children) Not being centralized has nothing to do with being trustless. The fediverse is also decentralized, yet you, me and everyone else has to log in to a specific server. If I try to login via lemmy.world, it'll fail. I have to login via programming.dev. Does that make lemmy and the fediverse trustless? No. Even the top answer on that SO question explains that the use case of hash trees for git is different from that of blockchain permalink fedilink source parent hideshow 4 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago (3 children) yeah, but this SO post has many up voted comments supporting my points as well. permalink fedilink source parent hideshow 3 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago 183 votes for your "similar but not the same" and 103 votes for "they are the same". At the very least, I'd say this is far from settled fact permalink fedilink source parent [–] ICastFist@programming.dev 1 point 2 years ago (1 child) You're completely ignoring the point that being decentralized and/or implementing hash trees does not make a system trustless permalink fedilink source parent hideshow 1 child comment replies: [–] simplymath@lemmy.world 2 points 2 years ago no, no. I'm conceding that-- not ignoring that. permalink fedilink source parent
[–] ICastFist@programming.dev 3 points 2 years ago (10 children) It’s trust less in the sense that commits can’t be easily forged and are signed with cryptographic keys and identities. I'm pretty sure being able to verify that the person responsible for a push is an actual maintainer is the opposite of trustless. permalink fedilink source parent hideshow 10 child comments replies: [–] simplymath@lemmy.world 2 points 2 years ago* (last edited 2 years ago) (9 children) How is it any different than verifying that a transaction occurred? How is a trusted repository different from a hard fork? Isn't "proving someone is a maintainer" just an IRL proof of stake? permalink fedilink source parent hideshow 9 child comments replies: [–] ICastFist@programming.dev 3 points 2 years ago (8 children) How is it any different than verifying that a transaction occurred? With a centralized trust source (bank), you ask for the records. How is a trusted repository different from a hard fork? Because you check who owns and maintains it. A notable example was with Simple Apps for Android, earlier this year the main repo was sold to a company. Trust was lost, thus a fork was created to keep the original stuff. permalink fedilink source parent hideshow 8 child comments replies: [–] simplymath@lemmy.world 2 points 2 years ago (7 children) Right, but isn't the "main chain" of Ethereum based on a similar principle wherein it's the main chain because it's the one the devs use? What about BTC vs BTC lightning. I'm genuinely failing to see a distinction here, and, again, the wiki article says that blockchains are special cases of Merkle trees. permalink fedilink source parent hideshow 7 child comments replies: [–] ICastFist@programming.dev 2 points 2 years ago (6 children) Right, but isn’t the “main chain” of Ethereum based on a similar principle wherein it’s the main chain because it’s the one the devs use? No clue, I don't keep an eye on that, I'm partially aware that there are several similar forks (and eth classic was a result of scammy shenanigans) but, afaict, none try to pretend they're the "real" ethereum. I’m genuinely failing to see a distinction here A distinction between trust and trustless? Because my initial point was that git isn't trustless, because it works just like any other online system that requires a login, where a central server/database checks if the user sending inputs was properly identified by some mean (password, cryptographic key, something else). Implementing a Merkle or any other hash tree doesn't make something trustless permalink fedilink source parent hideshow 6 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago (5 children) does git require authentication with a central server? I know that's common practice and true of github, but my recollection was that it was meant to fix the problem of distributed kernel development via an email listserv in the early 2000s. This stack exchange post discusses how it's not really centralized permalink fedilink source parent hideshow 5 child comments replies: [–] ICastFist@programming.dev 1 point 2 years ago (4 children) Not being centralized has nothing to do with being trustless. The fediverse is also decentralized, yet you, me and everyone else has to log in to a specific server. If I try to login via lemmy.world, it'll fail. I have to login via programming.dev. Does that make lemmy and the fediverse trustless? No. Even the top answer on that SO question explains that the use case of hash trees for git is different from that of blockchain permalink fedilink source parent hideshow 4 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago (3 children) yeah, but this SO post has many up voted comments supporting my points as well. permalink fedilink source parent hideshow 3 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago 183 votes for your "similar but not the same" and 103 votes for "they are the same". At the very least, I'd say this is far from settled fact permalink fedilink source parent [–] ICastFist@programming.dev 1 point 2 years ago (1 child) You're completely ignoring the point that being decentralized and/or implementing hash trees does not make a system trustless permalink fedilink source parent hideshow 1 child comment replies: [–] simplymath@lemmy.world 2 points 2 years ago no, no. I'm conceding that-- not ignoring that. permalink fedilink source parent
[–] simplymath@lemmy.world 2 points 2 years ago* (last edited 2 years ago) (9 children) How is it any different than verifying that a transaction occurred? How is a trusted repository different from a hard fork? Isn't "proving someone is a maintainer" just an IRL proof of stake? permalink fedilink source parent hideshow 9 child comments replies: [–] ICastFist@programming.dev 3 points 2 years ago (8 children) How is it any different than verifying that a transaction occurred? With a centralized trust source (bank), you ask for the records. How is a trusted repository different from a hard fork? Because you check who owns and maintains it. A notable example was with Simple Apps for Android, earlier this year the main repo was sold to a company. Trust was lost, thus a fork was created to keep the original stuff. permalink fedilink source parent hideshow 8 child comments replies: [–] simplymath@lemmy.world 2 points 2 years ago (7 children) Right, but isn't the "main chain" of Ethereum based on a similar principle wherein it's the main chain because it's the one the devs use? What about BTC vs BTC lightning. I'm genuinely failing to see a distinction here, and, again, the wiki article says that blockchains are special cases of Merkle trees. permalink fedilink source parent hideshow 7 child comments replies: [–] ICastFist@programming.dev 2 points 2 years ago (6 children) Right, but isn’t the “main chain” of Ethereum based on a similar principle wherein it’s the main chain because it’s the one the devs use? No clue, I don't keep an eye on that, I'm partially aware that there are several similar forks (and eth classic was a result of scammy shenanigans) but, afaict, none try to pretend they're the "real" ethereum. I’m genuinely failing to see a distinction here A distinction between trust and trustless? Because my initial point was that git isn't trustless, because it works just like any other online system that requires a login, where a central server/database checks if the user sending inputs was properly identified by some mean (password, cryptographic key, something else). Implementing a Merkle or any other hash tree doesn't make something trustless permalink fedilink source parent hideshow 6 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago (5 children) does git require authentication with a central server? I know that's common practice and true of github, but my recollection was that it was meant to fix the problem of distributed kernel development via an email listserv in the early 2000s. This stack exchange post discusses how it's not really centralized permalink fedilink source parent hideshow 5 child comments replies: [–] ICastFist@programming.dev 1 point 2 years ago (4 children) Not being centralized has nothing to do with being trustless. The fediverse is also decentralized, yet you, me and everyone else has to log in to a specific server. If I try to login via lemmy.world, it'll fail. I have to login via programming.dev. Does that make lemmy and the fediverse trustless? No. Even the top answer on that SO question explains that the use case of hash trees for git is different from that of blockchain permalink fedilink source parent hideshow 4 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago (3 children) yeah, but this SO post has many up voted comments supporting my points as well. permalink fedilink source parent hideshow 3 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago 183 votes for your "similar but not the same" and 103 votes for "they are the same". At the very least, I'd say this is far from settled fact permalink fedilink source parent [–] ICastFist@programming.dev 1 point 2 years ago (1 child) You're completely ignoring the point that being decentralized and/or implementing hash trees does not make a system trustless permalink fedilink source parent hideshow 1 child comment replies: [–] simplymath@lemmy.world 2 points 2 years ago no, no. I'm conceding that-- not ignoring that. permalink fedilink source parent
[–] ICastFist@programming.dev 3 points 2 years ago (8 children) How is it any different than verifying that a transaction occurred? With a centralized trust source (bank), you ask for the records. How is a trusted repository different from a hard fork? Because you check who owns and maintains it. A notable example was with Simple Apps for Android, earlier this year the main repo was sold to a company. Trust was lost, thus a fork was created to keep the original stuff. permalink fedilink source parent hideshow 8 child comments replies: [–] simplymath@lemmy.world 2 points 2 years ago (7 children) Right, but isn't the "main chain" of Ethereum based on a similar principle wherein it's the main chain because it's the one the devs use? What about BTC vs BTC lightning. I'm genuinely failing to see a distinction here, and, again, the wiki article says that blockchains are special cases of Merkle trees. permalink fedilink source parent hideshow 7 child comments replies: [–] ICastFist@programming.dev 2 points 2 years ago (6 children) Right, but isn’t the “main chain” of Ethereum based on a similar principle wherein it’s the main chain because it’s the one the devs use? No clue, I don't keep an eye on that, I'm partially aware that there are several similar forks (and eth classic was a result of scammy shenanigans) but, afaict, none try to pretend they're the "real" ethereum. I’m genuinely failing to see a distinction here A distinction between trust and trustless? Because my initial point was that git isn't trustless, because it works just like any other online system that requires a login, where a central server/database checks if the user sending inputs was properly identified by some mean (password, cryptographic key, something else). Implementing a Merkle or any other hash tree doesn't make something trustless permalink fedilink source parent hideshow 6 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago (5 children) does git require authentication with a central server? I know that's common practice and true of github, but my recollection was that it was meant to fix the problem of distributed kernel development via an email listserv in the early 2000s. This stack exchange post discusses how it's not really centralized permalink fedilink source parent hideshow 5 child comments replies: [–] ICastFist@programming.dev 1 point 2 years ago (4 children) Not being centralized has nothing to do with being trustless. The fediverse is also decentralized, yet you, me and everyone else has to log in to a specific server. If I try to login via lemmy.world, it'll fail. I have to login via programming.dev. Does that make lemmy and the fediverse trustless? No. Even the top answer on that SO question explains that the use case of hash trees for git is different from that of blockchain permalink fedilink source parent hideshow 4 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago (3 children) yeah, but this SO post has many up voted comments supporting my points as well. permalink fedilink source parent hideshow 3 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago 183 votes for your "similar but not the same" and 103 votes for "they are the same". At the very least, I'd say this is far from settled fact permalink fedilink source parent [–] ICastFist@programming.dev 1 point 2 years ago (1 child) You're completely ignoring the point that being decentralized and/or implementing hash trees does not make a system trustless permalink fedilink source parent hideshow 1 child comment replies: [–] simplymath@lemmy.world 2 points 2 years ago no, no. I'm conceding that-- not ignoring that. permalink fedilink source parent
[–] simplymath@lemmy.world 2 points 2 years ago (7 children) Right, but isn't the "main chain" of Ethereum based on a similar principle wherein it's the main chain because it's the one the devs use? What about BTC vs BTC lightning. I'm genuinely failing to see a distinction here, and, again, the wiki article says that blockchains are special cases of Merkle trees. permalink fedilink source parent hideshow 7 child comments replies: [–] ICastFist@programming.dev 2 points 2 years ago (6 children) Right, but isn’t the “main chain” of Ethereum based on a similar principle wherein it’s the main chain because it’s the one the devs use? No clue, I don't keep an eye on that, I'm partially aware that there are several similar forks (and eth classic was a result of scammy shenanigans) but, afaict, none try to pretend they're the "real" ethereum. I’m genuinely failing to see a distinction here A distinction between trust and trustless? Because my initial point was that git isn't trustless, because it works just like any other online system that requires a login, where a central server/database checks if the user sending inputs was properly identified by some mean (password, cryptographic key, something else). Implementing a Merkle or any other hash tree doesn't make something trustless permalink fedilink source parent hideshow 6 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago (5 children) does git require authentication with a central server? I know that's common practice and true of github, but my recollection was that it was meant to fix the problem of distributed kernel development via an email listserv in the early 2000s. This stack exchange post discusses how it's not really centralized permalink fedilink source parent hideshow 5 child comments replies: [–] ICastFist@programming.dev 1 point 2 years ago (4 children) Not being centralized has nothing to do with being trustless. The fediverse is also decentralized, yet you, me and everyone else has to log in to a specific server. If I try to login via lemmy.world, it'll fail. I have to login via programming.dev. Does that make lemmy and the fediverse trustless? No. Even the top answer on that SO question explains that the use case of hash trees for git is different from that of blockchain permalink fedilink source parent hideshow 4 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago (3 children) yeah, but this SO post has many up voted comments supporting my points as well. permalink fedilink source parent hideshow 3 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago 183 votes for your "similar but not the same" and 103 votes for "they are the same". At the very least, I'd say this is far from settled fact permalink fedilink source parent [–] ICastFist@programming.dev 1 point 2 years ago (1 child) You're completely ignoring the point that being decentralized and/or implementing hash trees does not make a system trustless permalink fedilink source parent hideshow 1 child comment replies: [–] simplymath@lemmy.world 2 points 2 years ago no, no. I'm conceding that-- not ignoring that. permalink fedilink source parent
[–] ICastFist@programming.dev 2 points 2 years ago (6 children) Right, but isn’t the “main chain” of Ethereum based on a similar principle wherein it’s the main chain because it’s the one the devs use? No clue, I don't keep an eye on that, I'm partially aware that there are several similar forks (and eth classic was a result of scammy shenanigans) but, afaict, none try to pretend they're the "real" ethereum. I’m genuinely failing to see a distinction here A distinction between trust and trustless? Because my initial point was that git isn't trustless, because it works just like any other online system that requires a login, where a central server/database checks if the user sending inputs was properly identified by some mean (password, cryptographic key, something else). Implementing a Merkle or any other hash tree doesn't make something trustless permalink fedilink source parent hideshow 6 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago (5 children) does git require authentication with a central server? I know that's common practice and true of github, but my recollection was that it was meant to fix the problem of distributed kernel development via an email listserv in the early 2000s. This stack exchange post discusses how it's not really centralized permalink fedilink source parent hideshow 5 child comments replies: [–] ICastFist@programming.dev 1 point 2 years ago (4 children) Not being centralized has nothing to do with being trustless. The fediverse is also decentralized, yet you, me and everyone else has to log in to a specific server. If I try to login via lemmy.world, it'll fail. I have to login via programming.dev. Does that make lemmy and the fediverse trustless? No. Even the top answer on that SO question explains that the use case of hash trees for git is different from that of blockchain permalink fedilink source parent hideshow 4 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago (3 children) yeah, but this SO post has many up voted comments supporting my points as well. permalink fedilink source parent hideshow 3 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago 183 votes for your "similar but not the same" and 103 votes for "they are the same". At the very least, I'd say this is far from settled fact permalink fedilink source parent [–] ICastFist@programming.dev 1 point 2 years ago (1 child) You're completely ignoring the point that being decentralized and/or implementing hash trees does not make a system trustless permalink fedilink source parent hideshow 1 child comment replies: [–] simplymath@lemmy.world 2 points 2 years ago no, no. I'm conceding that-- not ignoring that. permalink fedilink source parent
[–] simplymath@lemmy.world 1 point 2 years ago (5 children) does git require authentication with a central server? I know that's common practice and true of github, but my recollection was that it was meant to fix the problem of distributed kernel development via an email listserv in the early 2000s. This stack exchange post discusses how it's not really centralized permalink fedilink source parent hideshow 5 child comments replies: [–] ICastFist@programming.dev 1 point 2 years ago (4 children) Not being centralized has nothing to do with being trustless. The fediverse is also decentralized, yet you, me and everyone else has to log in to a specific server. If I try to login via lemmy.world, it'll fail. I have to login via programming.dev. Does that make lemmy and the fediverse trustless? No. Even the top answer on that SO question explains that the use case of hash trees for git is different from that of blockchain permalink fedilink source parent hideshow 4 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago (3 children) yeah, but this SO post has many up voted comments supporting my points as well. permalink fedilink source parent hideshow 3 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago 183 votes for your "similar but not the same" and 103 votes for "they are the same". At the very least, I'd say this is far from settled fact permalink fedilink source parent [–] ICastFist@programming.dev 1 point 2 years ago (1 child) You're completely ignoring the point that being decentralized and/or implementing hash trees does not make a system trustless permalink fedilink source parent hideshow 1 child comment replies: [–] simplymath@lemmy.world 2 points 2 years ago no, no. I'm conceding that-- not ignoring that. permalink fedilink source parent
[–] ICastFist@programming.dev 1 point 2 years ago (4 children) Not being centralized has nothing to do with being trustless. The fediverse is also decentralized, yet you, me and everyone else has to log in to a specific server. If I try to login via lemmy.world, it'll fail. I have to login via programming.dev. Does that make lemmy and the fediverse trustless? No. Even the top answer on that SO question explains that the use case of hash trees for git is different from that of blockchain permalink fedilink source parent hideshow 4 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago (3 children) yeah, but this SO post has many up voted comments supporting my points as well. permalink fedilink source parent hideshow 3 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago 183 votes for your "similar but not the same" and 103 votes for "they are the same". At the very least, I'd say this is far from settled fact permalink fedilink source parent [–] ICastFist@programming.dev 1 point 2 years ago (1 child) You're completely ignoring the point that being decentralized and/or implementing hash trees does not make a system trustless permalink fedilink source parent hideshow 1 child comment replies: [–] simplymath@lemmy.world 2 points 2 years ago no, no. I'm conceding that-- not ignoring that. permalink fedilink source parent
[–] simplymath@lemmy.world 1 point 2 years ago (3 children) yeah, but this SO post has many up voted comments supporting my points as well. permalink fedilink source parent hideshow 3 child comments replies: [–] simplymath@lemmy.world 1 point 2 years ago 183 votes for your "similar but not the same" and 103 votes for "they are the same". At the very least, I'd say this is far from settled fact permalink fedilink source parent [–] ICastFist@programming.dev 1 point 2 years ago (1 child) You're completely ignoring the point that being decentralized and/or implementing hash trees does not make a system trustless permalink fedilink source parent hideshow 1 child comment replies: [–] simplymath@lemmy.world 2 points 2 years ago no, no. I'm conceding that-- not ignoring that. permalink fedilink source parent
[–] simplymath@lemmy.world 1 point 2 years ago 183 votes for your "similar but not the same" and 103 votes for "they are the same". At the very least, I'd say this is far from settled fact permalink fedilink source parent
[–] ICastFist@programming.dev 1 point 2 years ago (1 child) You're completely ignoring the point that being decentralized and/or implementing hash trees does not make a system trustless permalink fedilink source parent hideshow 1 child comment replies: [–] simplymath@lemmy.world 2 points 2 years ago no, no. I'm conceding that-- not ignoring that. permalink fedilink source parent
[–] simplymath@lemmy.world 2 points 2 years ago no, no. I'm conceding that-- not ignoring that. permalink fedilink source parent
[–] simplymath@lemmy.world 1 point 2 years ago We define "blockchain" and "blockchain network", and then discuss two very different, well known classes of blockchain networks: cryptocurrencies and Git repositories. https://arxiv.org/abs/1803.00892 permalink fedilink source parent