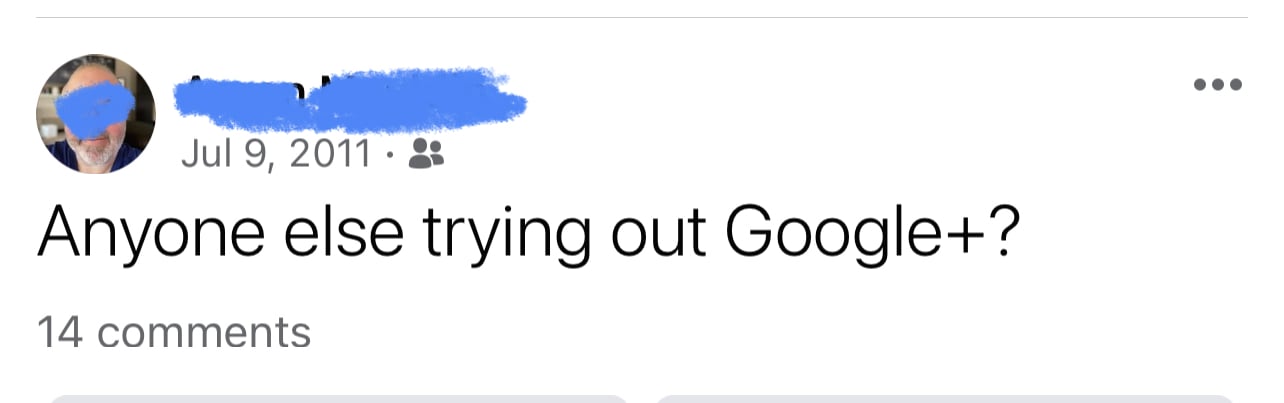
▲ 1355 ▼ 12 years ago. Wonder what Lemmy will look like in 12 years? (lemmy.world) submitted 3 years ago by mysoulishome@lemmy.world to c/fediverse@lemmy.world 327 comments fedilink hide all child comments
[–] jelloeater85@lemmy.world 1 point 3 years ago (2 children) You would have to run your own CA and get everyone to install your root cert on their devices. That what happens already with tech like smart cards and SSL inspection firewalls. It's all about trusting the connection implicitly. permalink fedilink source parent hideshow 2 child comments replies: [–] Agent641@lemmy.world 2 points 3 years ago (1 child) "Mate I dont trust you" "Its okay, I have a certificate" "This just says 'Trust me bro' and has your name at the bottom." "If you still dont trust me, just call this guy, he will vouch for me!" "This is your own phone number." permalink fedilink source parent hideshow 1 child comment replies: [–] jelloeater85@lemmy.world 1 point 3 years ago Yup! 😂 permalink fedilink source parent
[–] Agent641@lemmy.world 2 points 3 years ago (1 child) "Mate I dont trust you" "Its okay, I have a certificate" "This just says 'Trust me bro' and has your name at the bottom." "If you still dont trust me, just call this guy, he will vouch for me!" "This is your own phone number." permalink fedilink source parent hideshow 1 child comment replies: [–] jelloeater85@lemmy.world 1 point 3 years ago Yup! 😂 permalink fedilink source parent