Don't tell me people are using llms to generate passwords
post
replies:
Welp, that's another thing I hadn't thought you could use llms for and another thing I would never do
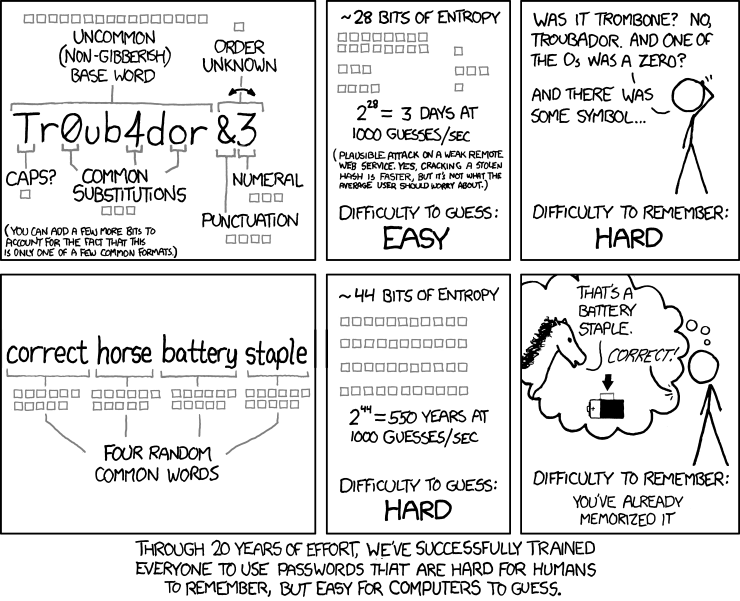
Why not do this....
Corect horse battery staple
replies:
LLM-generated passwords
This is akin to asking Karen from accounting to generate a password for you, and trusting that it will be a true random and secure password and that she won't yap about it to everyone.
That statement is one of the painfully dumbest things I've read in my life, and I've read the bible.
Irregular ? Like my bowel movements ?
Not again this horrible web design/engine whatever laggin/stuttering the way it almost induce a epileptic seizure in me.
all 17 comments