I tried testing a movie from my home server in plex through firefox and repeatedly got this message, even after reloading.

I knew that they had paywalled the apps on mobile and streaming from outside the network but now they have also blocked watching your own movies through your own hardware.

I do get the point that making software should be able to sustain people but I dont see the move of plex as a fair thing to do. Yes, they have made great software but taking your home server hostage feels like the wrong move.

Even a pop up that says "we need you to donate please" would have been fine. make it pop up before every movie, play donation ads before any movie but straight up disabling the app is kinda cruel.

Anyway, i have switched to jellyfin and it is insanely good. please give it a try. you can run it alongside plex with not issues (at least i had none) and compare the two.

In any case, good luck. Let me know if you need help.
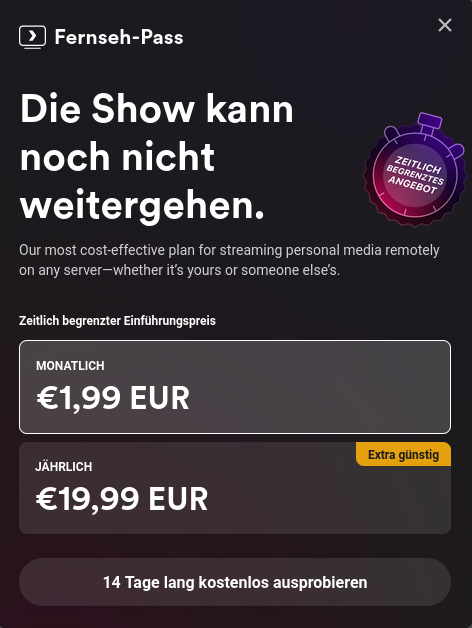
Screenshot of a pop up in plex media center saying "die show kann noch nicht weitergehen" which means the show cant go on yet. below are pricing options to buy a subscription. this is displayed on a home server in the same network. plex has worked for years.
you are viewing a single comment's thread
view the rest of the comments
[–] 38 points 1 year ago (40 children)

Old news, but time for Jellyfin. I made the switch a couple months ago. Some minor teething issues, but better, IMO, especially now as my family all have LDAP users and that just works.

  • source
  • hideshow 40 child comments
  • [–] 3 points 1 year ago (7 children)

    I made the switch a few months back as well. Have you had the issue where"Recently Added" just straight up doesn't work? It's about 50/50 for me whether my new downloads show up there or not, and if they do, it's usually inserted somewhere down the list between other things I added months ago. Not sure if there's a workaround, but it's my #1 complaint with Jellyfin. Otherwise, it's been great.

  • source
  • parent
  • hideshow 7 child comments
  • [–] 3 points 1 year ago (6 children)

    How is your underlying file system set up?

  • source
  • parent
  • hideshow 6 child comments
  • [–] 1 point 1 year ago* (last edited 1 year ago) (5 children)

    It's an Unraid share on a local NAS, and the array is formatted as xfs.

  • source
  • parent
  • hideshow 5 child comments
  • [–] 1 point 1 year ago (4 children)
  • [–] 1 point 1 year ago (3 children)

    I'm actually not 100% sure how to answer that. It's just a "share" configured through the Unraid UI, being accessed by a docker container running on the same machine (binhex's Jellyfin image.) I think that the "share" in this context is essentially just a mount point, but it's also (optionally) exposed as an SMB share externally.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 2 points 1 year ago (2 children)

    Ahh OK, a Docker bind. 3 things to check:

    1. That you added the folders in that weird way Unraod requires, see: https://forum.jellyfin.org/t-solved-jellyfin-not-detecting-media-in-unraid (this probably isn't it, but worth checking)

    2. Make sure for newly added, Jellyfin is configured for Date File Scanned into Library, vs the Created Date on the file

    3. Ensure the Arrs aren't set to change the date on file import. By default they modify created/modified dates to be the release date, which can put things in an unexpected order.

  • source
  • parent
  • hideshow 2 child comments
  • [–] [S] 3 points 1 year ago (28 children)

    awesome. thanks for chiming in. I will have to check how to do external streaming without opening my network up to the world (metaphorically).

  • source
  • parent
  • hideshow 28 child comments
  • [–] 9 points 1 year ago* (last edited 1 year ago) (20 children)

    ...wireguard

    (there are android TV apps for wireguard, not that any normie can actually move a client file to it and turn it on, or could be bothered to)

  • source
  • parent
  • hideshow 20 child comments
  • [–] [S] 4 points 1 year ago (19 children)

    Thats not what I meant. I of course have wireguard set up for administration and my own streaming needs. But friends of mine who were able to use plex by just making an account but now they cant because of course there is no relay server etc. I'll have to think of a way to make it available to them (easily!) without putting my network at risk.

  • source
  • parent
  • hideshow 19 child comments
  • [–] 5 points 1 year ago (11 children)
  • [–] [S] 3 points 1 year ago (4 children)

    That is pretty much how I imagined it. Sadly, its A TON of work. I have most of this set up in many VPSs for both me and customers (with other services of course) and I can imagine its probably the best solution. I still hate my life when thinking of implementing it. :D I bet its gonna be easier than I think but you may get my point here. Thank you very much for sharing.

  • source
  • parent
  • hideshow 4 child comments
  • [–] 3 points 1 year ago (3 children)

    Hell I know what you mean, it was so much trial and error until it worked, hence this guide/template to help others. Plus at some point it feels more like work than a hobby 😅

  • source
  • parent
  • hideshow 3 child comments
  • [–] 2 points 1 year ago (4 children)

    My primary worry for this is that something in the jellyfin stack gets an open vulnerability, like there's an overflow you can use on a post call to a piece of media allowing remote code execution.

    Tautulli had a leak once that provided the user's private token. Then there was a way in Plex with a private token to pull data from elsewhere on the server. That's how LastPass got nuked I hear.

  • source
  • parent
  • hideshow 4 child comments
  • [–] 2 points 1 year ago (3 children)

    I get you and I know that there can be security issues (especially in Jellyfin) that might give you access. This is the reason I only mount the media and config folders, and nothing else into the docker container. The media folders are mounted as read only and don't contain sensitive information. For the config folder I created a separate user. Plus I block non-German IP addresses which already blocks quite some bots. If your friends have fixed IP addresses you could also just whitelist them and block everything else.

    You could also probably sniff the network and define more strict rules on 'allowed' requests in fail2ban but this is bridle because requests might change with different versions.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 2 points 1 year ago (2 children)

    They actually do a small login f2b effort right in JF, but it appears to be quite limited.

    The container is more secure by default, and if people set up their docker well it reduces the dangers substantially. A lot of people don't go docker though.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 3 points 1 year ago (6 children)

    Mine is public, but I block every state but the one all of my users live in(family) and I never get unwanted visitors. Couldn't say the same if I lived in NY or CA.

    If they have static IP addresses, you may be able to whitelist them in your proxy, or maybe there's some sort of dyndns client/relay software you can run if their ips change.

  • source
  • parent
  • hideshow 6 child comments
  • [–] [S] 2 points 1 year ago (5 children)

    yeah, thanks. but thats not gonna work for me. i live in a big city and none of us (me and my server included) have static IPs nor am I gonna get them (at all) and I dont want to pay for them either (because ISPs here want you to pay for them). in any case, thanks for trying to suggest something. it might help someone else who has a different setup. :)

  • source
  • parent
  • hideshow 5 child comments
  • [–] 1 point 1 year ago (4 children)

    Welp, I guess they'll just have to start their own servers or you'll have to get out your credit card. Pity.

  • source
  • parent
  • hideshow 4 child comments
  • [–] [S] 0 points 1 year ago (3 children)

    yeah no. there are a lot of other solutions to this. they're just a little annoying. others have confirmed there are similar setups like plex is doing with a relay server, but selfhosted.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 2 points 1 year ago* (2 children)

    there are a lot of other solutions to this

    Jellyfin servers don't connect to eachother, or relay themselves to anything else beyond simple reverse proxies. I looked over the entire thread and didn't see anything but ldap and tailscale/wireguard suggestions.

    You said there were a lot of other solutions, so wherever those solutions are, I'm sure they'll work out. Good luck!🙃

  • source
  • parent
  • hideshow 2 child comments
  • [–] 2 points 1 year ago (3 children)

    I used synology and reverse proxy. It was pretty easy to set up. The tricky part was going into jellyfins setting and connecting your reverse proxy to the path you made.

    Overall my kids and family can now access it anywhere.

  • source
  • parent
  • hideshow 3 child comments
  • [–] [S] 2 points 1 year ago (2 children)

    I run a reverse proxy too. are you talking about a public one? I'm probably gonna use a relay server for it which essentially is the same I guess.

  • source
  • parent
  • hideshow 2 child comments
  • [–] 2 points 1 year ago (1 child)

    Can your router open ports from a hostname vs an IP? If so, clients could run dynamic DNS.

    WG client side isn't really that hard, though. All the fam run WG 24/7 on devices, and only traffic for the internal network goes through it.

  • source
  • parent
  • hideshow 1 child comment
  • [–] [S] 1 point 1 year ago

    I know. the issue is my friends dont have networks run by me. So I have to gain access to them and have to change setups which makes the situation likely to blow in my face. its just not a good solution imo. People have already suggested a relay server which will likely be the best solution.

  • source
  • parent
  • [–] 1 point 1 year ago (2 children)

    Give me a package that runs on my ds214play and I'll switch in a heartbeat

  • source
  • parent
  • hideshow 2 child comments
  • [–] 2 points 1 year ago (1 child)

    https://github.com/SynoCommunity/spksrc/issues/5941 ?

    I really wanted Jellyfin working in my DS214Play with DSM6, and I noticed that a package for these evansport CPUs doesn't exist and it's officially not supported, so I tried myself and I succeeded.

  • source
  • parent
  • hideshow 1 child comment
  • [–] 3 points 1 year ago

    Thanks for the link. It seems they got it somehow working on DSM6, but if I check the thread, it's a lot of ducttape and locktight involved especially to run with DSM7. Might try it out on a rainy sunday

  • source
  • parent