Hey,
currently I am at a loss with my setup and can't figure out whats going wrong. I'm preparing a migration of my private root server to my @Home Setup. The idea was to create a DMZ for all those Server with Public Internet Access and put them into a DMZ.
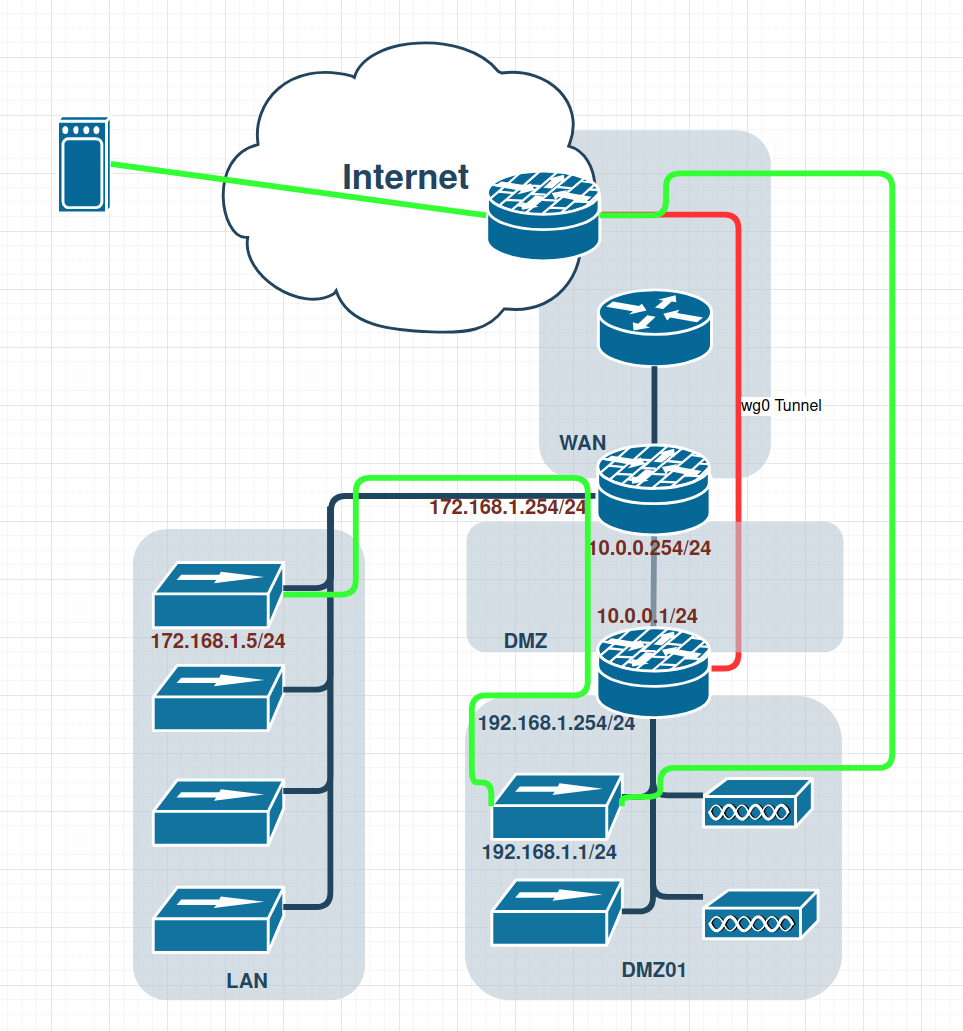
Now I got a Public OPNsense, some Modem from my ISP, a Unifi Dream Machine (that manages LAN and stuff) and another OPNsense inside my DMZ.
There is a Wireguard Tunnel connecting the two OPNsense, the local one got a 0.0.0.0/0 route as Peer Network.
If I now try to access any Website, managed by the Nginx Proxy 192.168.1.1/24, it works fine as long as the Website is inside the DMZ.
My Problem now is to make the green path happen to access stuff inside my LAN over the Public OPNsense.
The proxy is able to curl the LAN Websites and i can Ping and Trace all the IPs but something is broken. I can see the Packages arrive at the LAN website and make it back to the public OPNsense but my browser will always get a "timed out" :'(