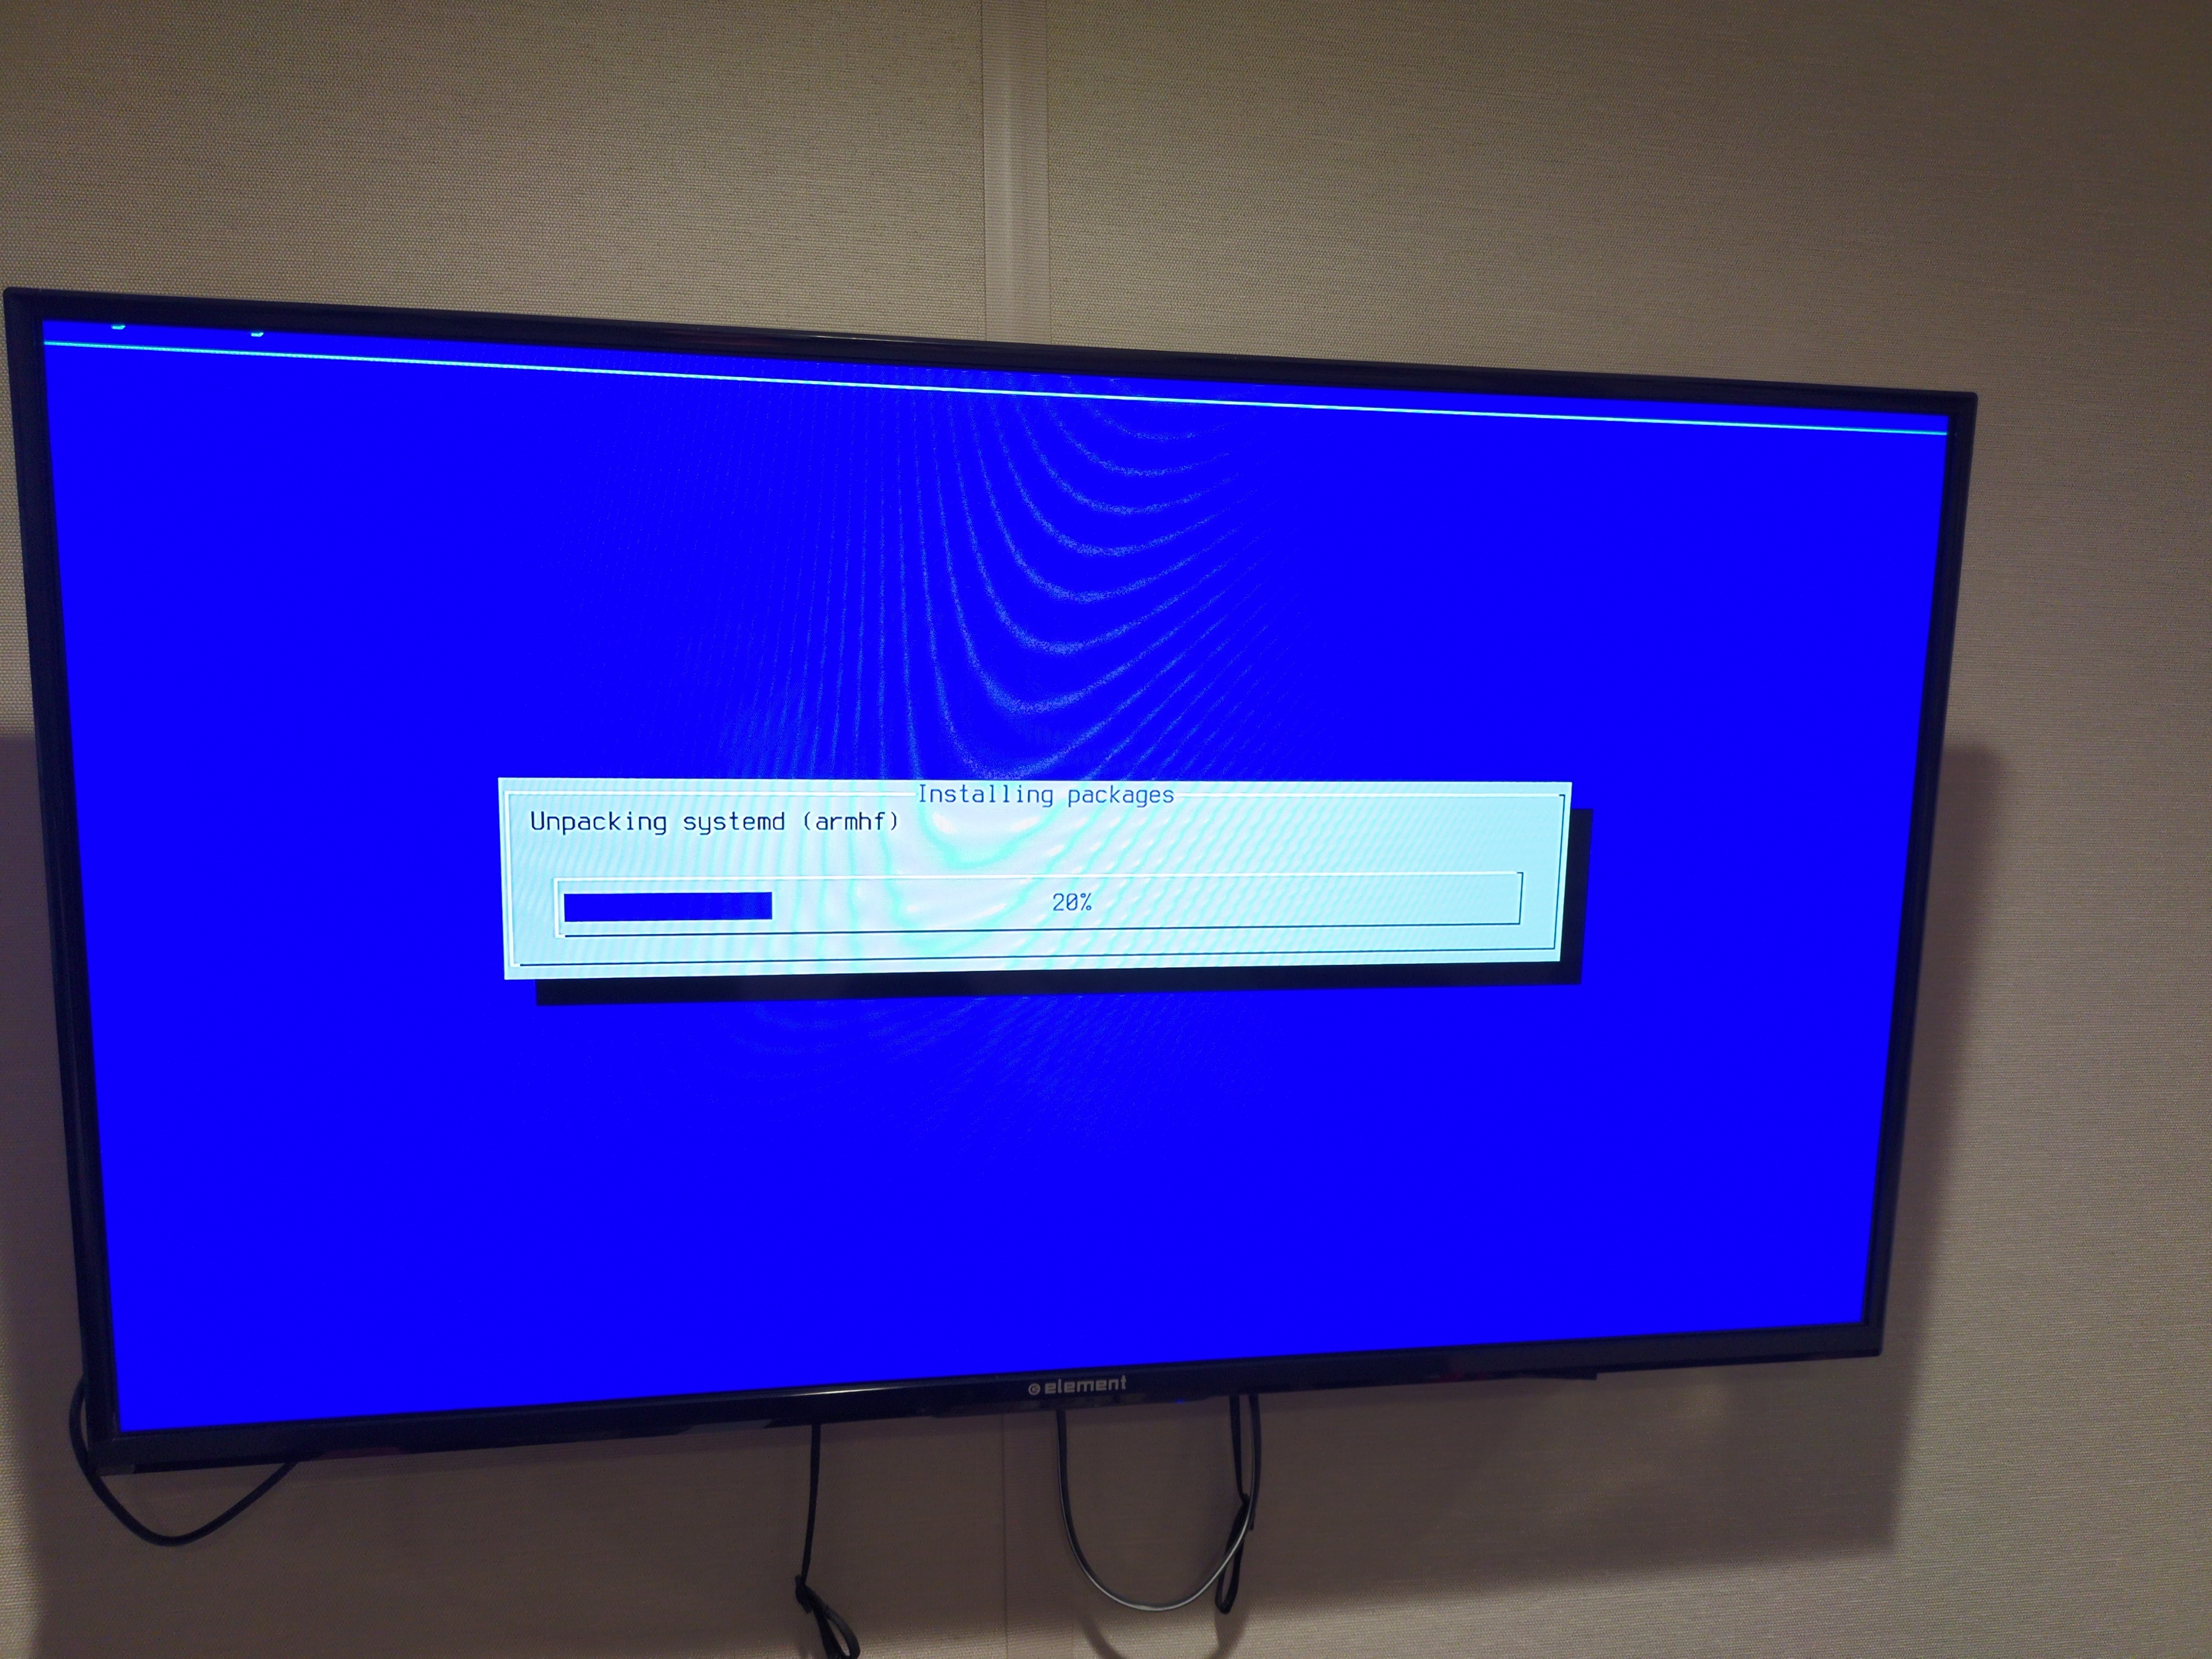
When I just see my TV taking Linux updates it makes me feel so cozy. For context sake I have a veroV running osmc.
When I just see my TV taking Linux updates it makes me feel so cozy. For context sake I have a veroV running osmc.
Well, my experience was
All in all, it works very contrary to my experience that layers upon layers leads to unmanageable complexity and inefficinecy and it's all implemented in a poor way, functionally (some will likely disagree to this).