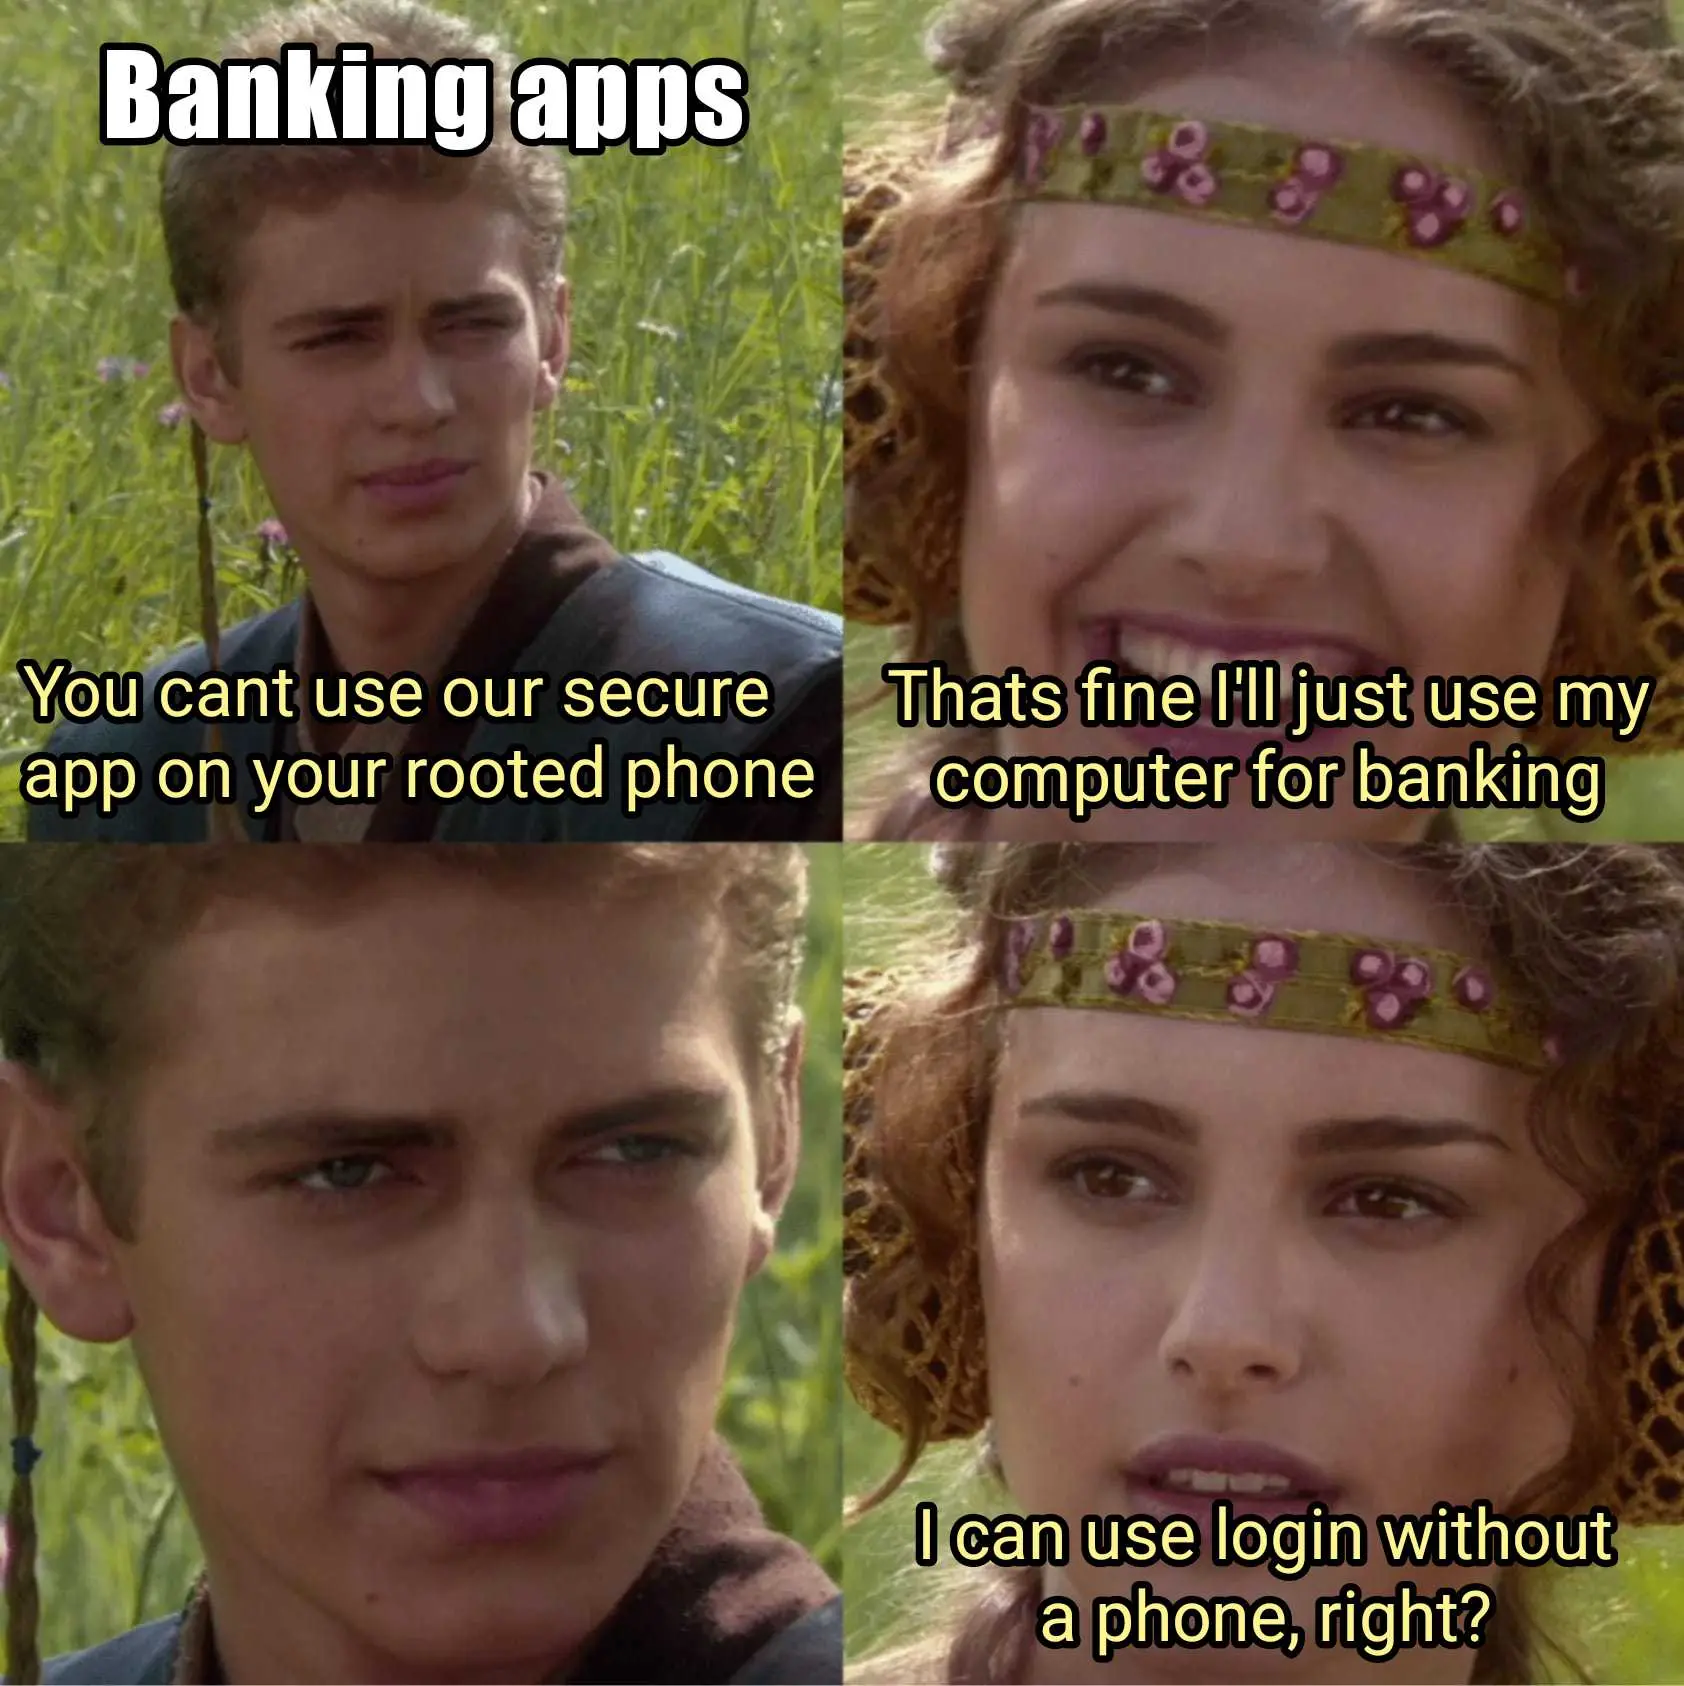
I'm lucky my banking app works (GrapheneOS), as it's now requiring 2FA with the app anytime I login on the browser. Can't use an actually secure form like TOTP. At least they now allow passwords over 8 characters (yes, serious).
(Meme in comments)
I'm lucky my banking app works (GrapheneOS), as it's now requiring 2FA with the app anytime I login on the browser. Can't use an actually secure form like TOTP. At least they now allow passwords over 8 characters (yes, serious).
(Meme in comments)
So obviously the saved state in the app wasn't actually expired, since it could still approve MFA requests. So what good is it expiring biometric auth if the app is still authorized to log me in effectively bypassing MFA?
I love this and hate this so much