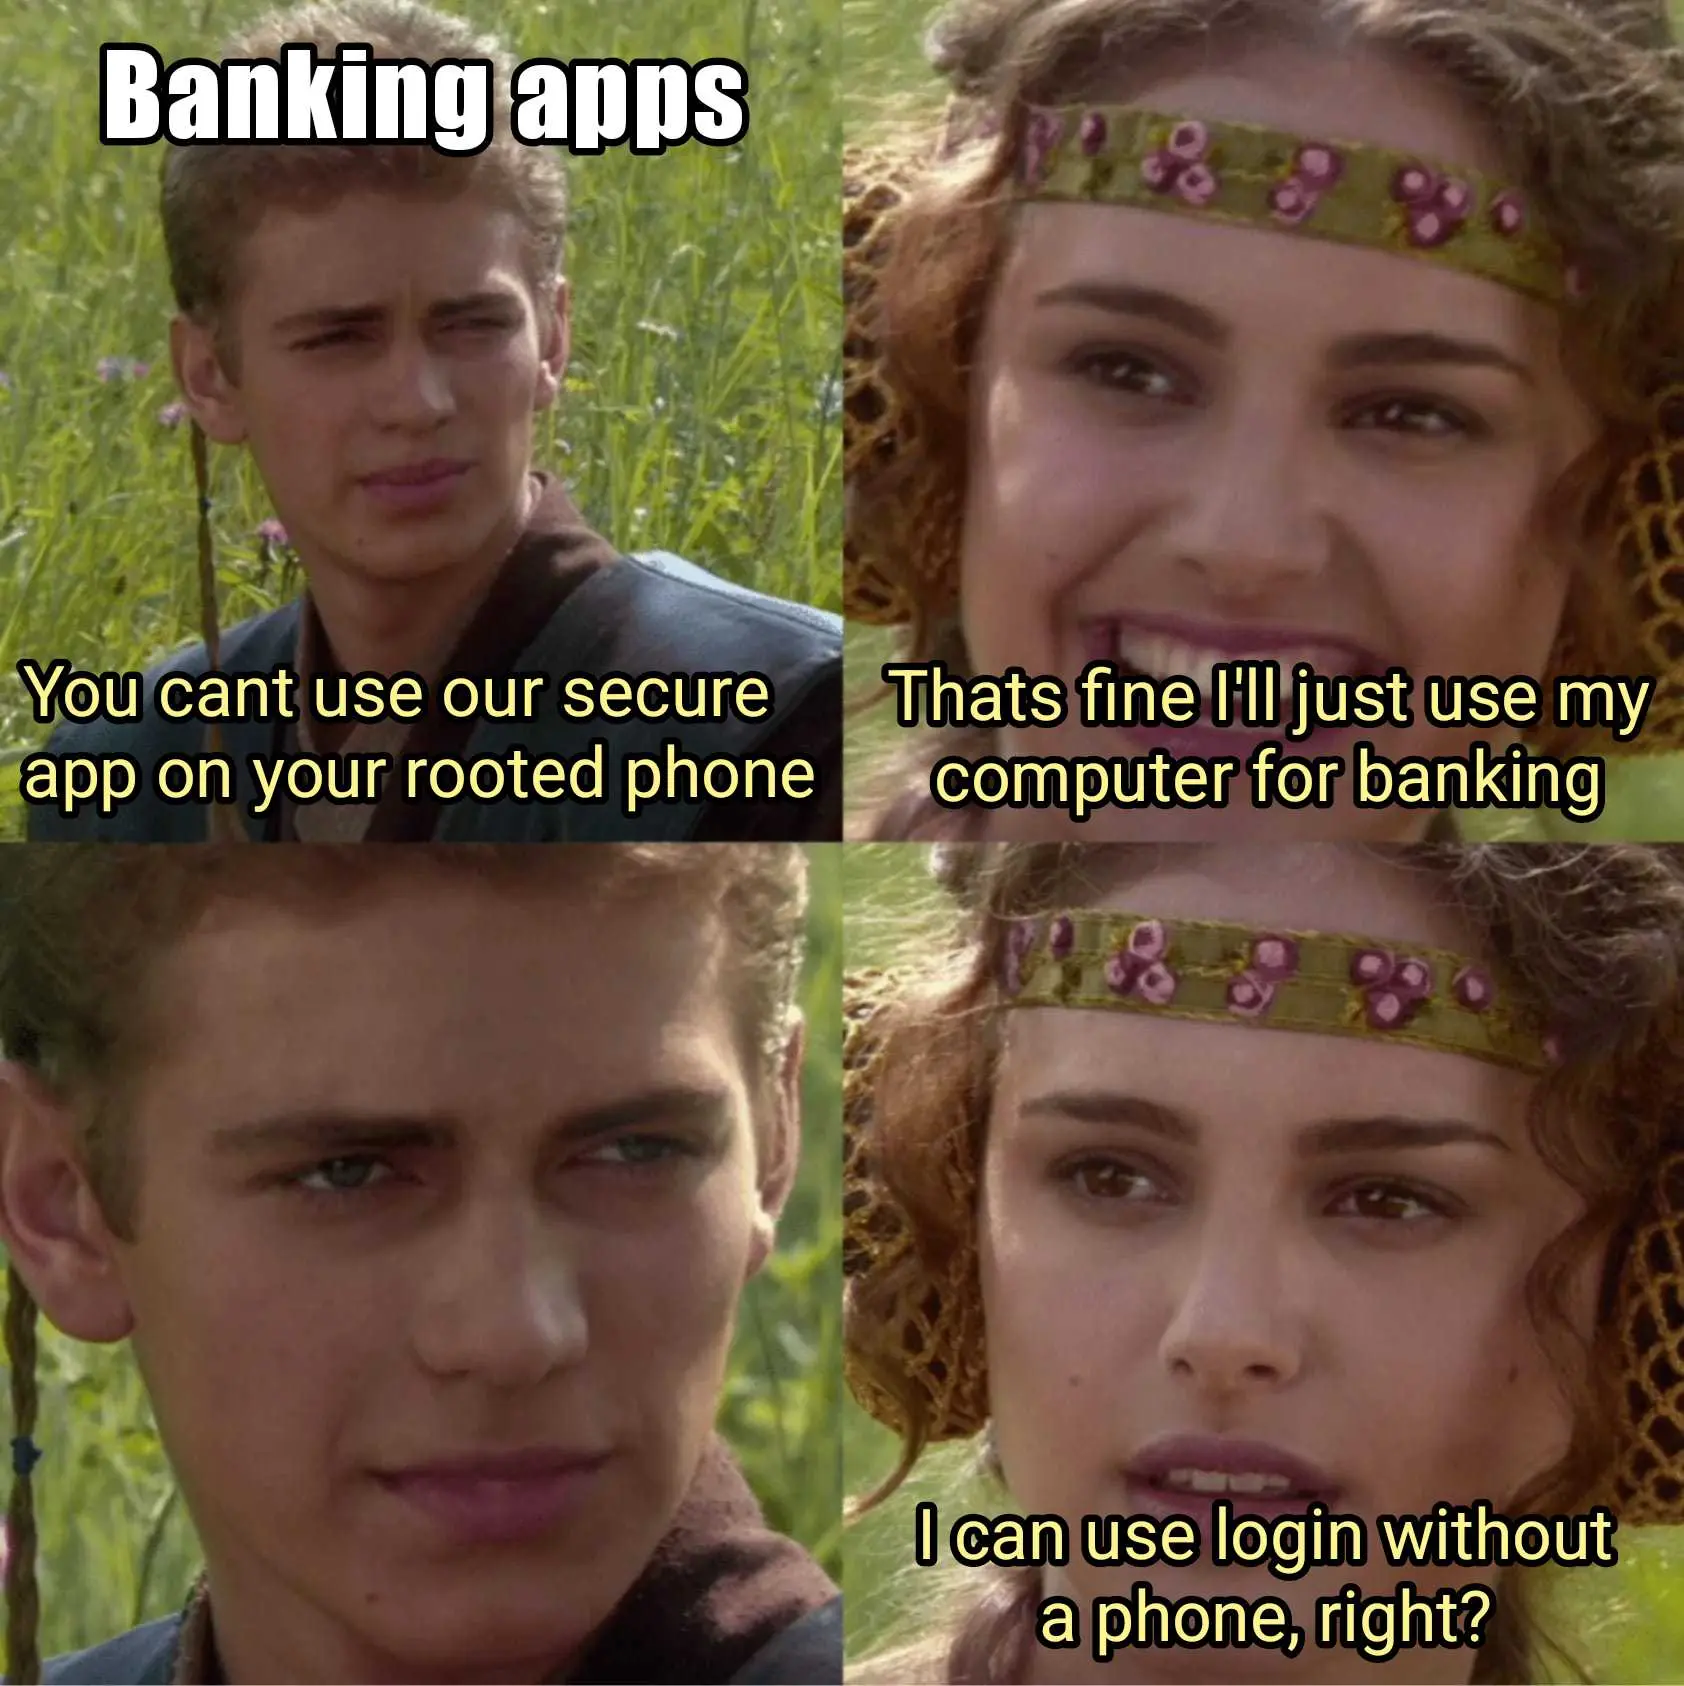
I'm lucky my banking app works (GrapheneOS), as it's now requiring 2FA with the app anytime I login on the browser. Can't use an actually secure form like TOTP. At least they now allow passwords over 8 characters (yes, serious).

(Meme in comments)
you are viewing a single comment's thread
view the rest of the comments
[–] [S] 3 points 2 years ago (2 children)

genuinely curious; can u elaborate on the deal with google?

  • source
  • parent
  • hideshow 2 child comments
  • [–] 2 points 2 years ago (1 child)

    Pure wild speculation if I'm honest, however I'd be more surprised if I was completely wrong. It's always seemed sketchy the way Google have basically said "Use our phone, it's more secure!" with their Nexus and Pixel phones - this was long after the time Google stopped not being evil. At best, the security problems have simply changed manufacturer. Also, Google have a history of undermining development of circumvention, eg hiring the developer of MicroG and forcing him to stop development as a term in his contract.

    The diva part is widely known, GrapheneOS developers don't play nice with the rest of the custom development community. So, while I can't substantiate any actual deal between them and Google, it's the perfect recipe.

  • source
  • parent
  • hideshow 1 child comment