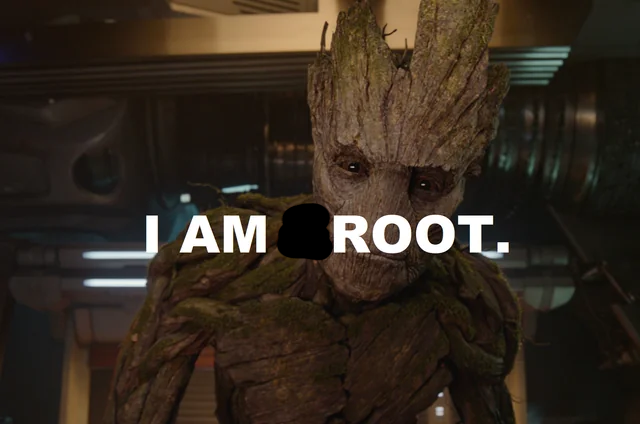
Shit meme, I know.

Groot from the hit Marvel movie "Avengers: Something" says "I am root." (The 'G' has been scribbled out in a very low effort as this is a low effort meme.)
you are viewing a single comment's thread
view the rest of the comments
[–] 24 points 1 year ago (14 children)

You get tired of playing Simon Says when you're doing a lot of admin stuff at once.

  • source
  • parent
  • hideshow 14 child comments
  • [–] 12 points 1 year ago (9 children)

    Well then still sudo -s would suffice, no?

  • source
  • parent
  • hideshow 9 child comments
  • [–] 7 points 1 year ago (8 children)
  • [–] 5 points 1 year ago (6 children)

    Having a password for root is Ill advised.

  • source
  • parent
  • hideshow 6 child comments
  • [–] 1 point 1 year ago (5 children)

    Maybe I'm a bit ignorant, but would it make much of a difference? Whether I authenticate with my own account to get root permissions or directly with root, I still have a string of characters which I use to get root priveleges on my machine. For a single (physical) user machine, that allows me to use a separate password for root. Should be better than using the same one twice, right?

  • source
  • parent
  • hideshow 5 child comments
  • [–] 5 points 1 year ago (4 children)

    If root has a password, it's only one password; everyone who has root access knows the password, which means that anyone can share it with no accountability. If privilege escalation rights are granted instead, it's easy to see who did what, as well as to contain any kind of compromise (by revoking said rights).

    Also, I think you originally referred to su but sudo allows much more granular control.

  • source
  • parent
  • hideshow 4 child comments
  • [–] 1 point 1 year ago (3 children)

    So, we are clearly talking about different environments here. Of course I would not have a password for root in an enterprize setting where you have a lot of different people managing one machine. But for your regular desktop computer with one user, it just complicates things needlessly without providing any benefits.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 1 point 1 year ago (2 children)

    Your home network is certainly less of a security risk due to both being a smaller target and (usually) needing to have fewer services available or ports open, so I would agree with you it's acceptable for security to be more lax. Personally, I don't find sudo to be less convenient than su; it's even saved me from thoughtlessly running a dangerous command a time or two. Also, I try to keep my home network setup close to my work network until doing so gets in the way. If nothing else, this prevents me from getting used to a different way of doing things.

    However, it's your network. If you find that your way works better for you, by all means, configure your system in whatever way seems best to you!

  • source
  • parent
  • hideshow 2 child comments
  • [–] 1 point 1 year ago (1 child)

    How did we arrive at networking? I feel like we are on two completely different pages.

    I was talking about your regular end user machines, what we usually call "desktop computers". They are connected to the internet, but I don't have any way to remotely login into those. And I have a single person per computer. There is no need to disable root passwords on these, seeing that Larry executed a command as root won't provide any insight, I know that Larry is the only person who uses the machine. And it can complicate things in a sense that if Larry fatfingers his password three times and gets locked out, I'll have to get into his filesystem somehow and remove tallies manually instead of just logging in as root and doing faillock --reset.

  • source
  • parent
  • hideshow 1 child comment
  • [–] 2 points 1 year ago

    Sorry if I was unclear; what you're saying is kind of my point. A computer without networking can still have risks, but they're a lot lower. The standards of security can change with conditions. If you have a computer on an enterprise network, it should be very secure; if on your home network, more cavalier standards can make sense. If you have a computer without any networking whatsoever, being compromised is not impossible, but it's much less likely unless you're storing something quite extraordinary on the system. That's why I referenced networks while talking about the configured security of an individual system. In general, I believe I was broadly agreeing with you.

  • source
  • parent
  • [–] -2 points 1 year ago (3 children)

    If you do multiple admin commands, sudo doesn't prompt for your password. There's some time limit before having to re input it.

    Logging in as root is bad security hygiene. You'll become complacent and leave it logged in at some point. That's how you get pwnd.

  • source
  • parent
  • hideshow 3 child comments
  • [–] 4 points 1 year ago

    I want to know more. Looking past running full desktop sessions as root and inputting stupid commands when sudo su, what's the problem with having a terminal window open and escalated to root?

  • source
  • parent
  • [–] 3 points 1 year ago* (last edited 1 year ago)

    There's some time limit before having to re input it.

    Inputting a password multiple times into sudo has downsides too. Larger window for attackers to do something like: add a directory to your path, which has a fake sudo in it, and capture your password.

  • source
  • parent